CERT Polska: fake DPD redelivery-fee phishing hosted on 96-126-126-164.cprapid.com
CERT Polska warns of fake DPD 'failed delivery' messages leading to a redelivery-fee page on 96-126-126-164.cprapid.com that steals payment card data.
- First reported
- Reports
- 1
Source: x.com · published
What happened
CERT Polska warned on X on 16 October 2026 of a new wave of a phishing campaign impersonating courier companies. Fraudsters send messages saying an attempt to deliver a parcel failed, with a link that supposedly lets the recipient arrange a new delivery date.
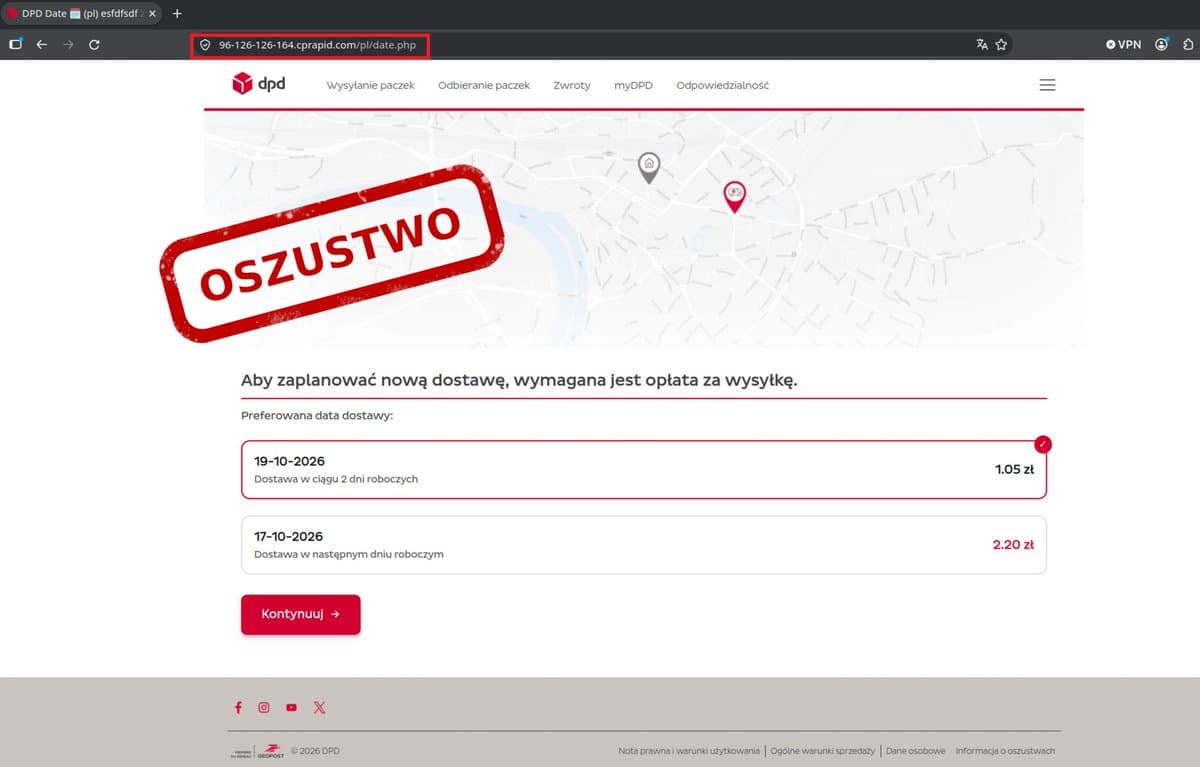
Screenshots shared by CERT Polska show an email from the sender 'INFO' <mail@toolbox-kaitori.com> with the subject 'DPD - Twoja paczka czeka - umow ponowna dostawe [REF:993101]' ('DPD - your parcel is waiting - arrange redelivery'), DPD Polska branding and a 'Umów ponowną dostawę' button. The sending address may belong to a compromised third party rather than the scammers. The linked pages are hosted on 96-126-126-164.cprapid.com (paths /pl/update.php, /pl/date.php and /pl/kasse.php) and display DPD branding and DPD's genuine contact address. DPD is the impersonated brand and is not involved.
How the scam works
CERT Polska says the link leads to a malicious website prepared by cybercriminals, which asks the victim to choose a new delivery date and pay a small redelivery surcharge; the screenshots show fees of 1.05 zł and 2.20 zł. The real aim is to steal payment card data, which can then be used for unauthorised transactions or further fraud attempts.
CERT Polska advises checking the address of a website before entering any data, and checking a parcel's status only on the courier's website that you have found yourself or in the carrier's official app. Suspicious messages and websites can be reported to CERT Polska through the form at incydent.cert.pl or the 'Bezpiecznie w sieci' service in the mObywatel app, which also helps protect other users.
Source
CERT Polska on X (@CERT_Polska), post of 16 October 2026.
Red flags
- A 'failed delivery' message asking you to pay a small fee to rearrange delivery.
- A courier page on a domain that isn't the courier's own (here a cprapid.com hostname).
- A sender address unrelated to the courier company.
If you were targeted
- 1Don't click the link or enter card details.
- 2Check parcel status on the courier's website found yourself, or in its official app.
- 3If you entered card details, call your bank to block the card.
- 4Report the message to CERT Polska at incydent.cert.pl or via 'Bezpiecznie w sieci' in the mObywatel app.