Fake 'Anthropic AI preview' invites lead to Google/Microsoft phish on us968web-zoom.us
Cofense reports fake "Anthropic AI preview" invitations, abusing GoTo Webinar and a Zapier link shortener, that lead to Google and Microsoft credential-phishing pages on lookalike domains.
- First reported
- Reports
- 1
Source: cofense.com · published
What happened
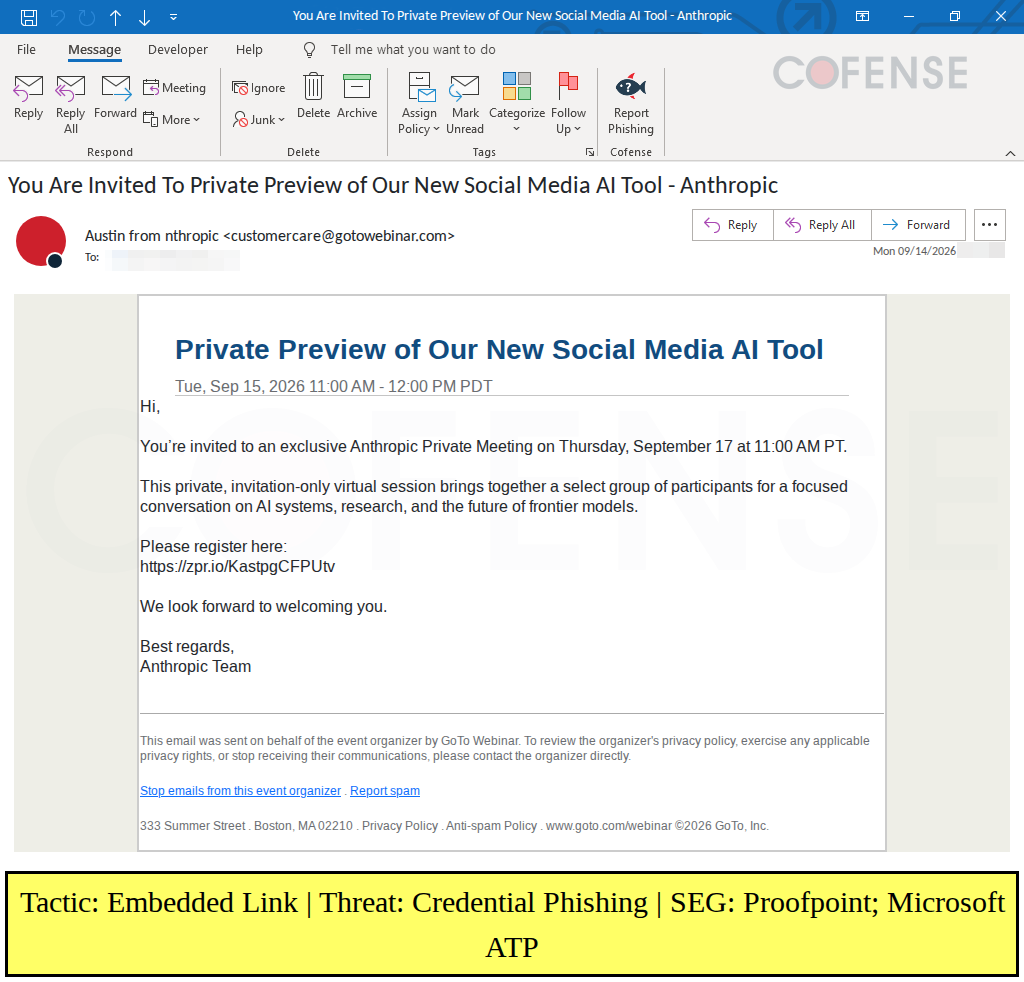
On 29 October 2026 Cofense published research on a credential-phishing campaign, running since September 2026, that sends emails posing as an exclusive invitation to a private Anthropic AI preview meeting. Anthropic, the company behind the Claude AI assistant, did not send these messages; it is the brand being impersonated. Cofense says the emails abuse the legitimate GoTo Webinar service (the sender address shows as GoTo Webinar's customer-care address, which has been abused before), use the sender name "Austin from nthropic" with the "A" missing, and link through an abused Zapier URL shortener (zpr.io).
How the scam works
The link first leads to a Cloudflare CAPTCHA, which keeps automated scanners away from the phishing page. A Zoom-spoofing registration page on us968web-zoom.us then appears, with the Anthropic meeting details, and asks the visitor to register with a work email using "Continue with Google" or "Continue with Microsoft". After a second, sliding CAPTCHA that Cofense says also blocks many security tools, the visitor sees a fake Google login on goo.gle-access-eventregister.icu or a fake Microsoft login on office.com-access-sharepoint.com. Cofense reports that the Google page captures only usernames, probably because of a misconfiguration, while the Microsoft page captures both usernames and passwords.
A stolen work login can give an attacker access to email and documents and a foothold for attacks on the rest of the organisation. Anthropic, Google, Microsoft, Zoom, GoTo and Zapier are impersonated or abused brands, not the operators. The giveaway signs are small mismatches: the email carries GoTo Webinar branding while the page shows Zoom branding, the sender name is misspelled, and the login pages sit on lookalike domains.
Source
Cofense Intelligence, "Would Your Employees Join a Fake Anthropic AI Preview?", 29 October 2026.
Red flags
- An invitation to a "private preview" of a new AI tool that you did not expect.
- A sender name with a spelling error ("Austin from nthropic") and a webinar-service email address.
- A shortened link (zpr.io) and a CAPTCHA before any content is shown.
- Branding that changes between email (GoTo Webinar) and web page (Zoom).
- Login pages on lookalike domains such as goo.gle-access-eventregister.icu or office.com-access-sharepoint.com.
If you were targeted
- 1Do not click "Continue with Google" or "Continue with Microsoft" on an event page reached from an unexpected email.
- 2Check the full address of any login page before entering credentials; real Google and Microsoft logins do not sit on these domains.
- 3If you entered a username or password, change it at once and review recent sign-ins; turn on multi-factor authentication.
- 4Report the email to your IT or security team and block the domains listed.
- 5Contact the company named in an invitation through its official website if you want to confirm an event.