Skip to content
Scammers.com
PhishingReviewed

Fake cPanel webmail login hosted on Cloudflare R2 bucket asks for email password

Automated URL scanner urlDNA posted on Mastodon (infosec.exchange) on 11 November 2026 that hxxps://pub-f2ec4aa4192d4950abc21ae9510403d4[.]r2[.]dev/still[.]html is a possible phishing page; the host is also on the Phi…

First reported
Reports
1

Source: infosec.exchange · published

Illustration: Phishing, texts and email scams

What happened

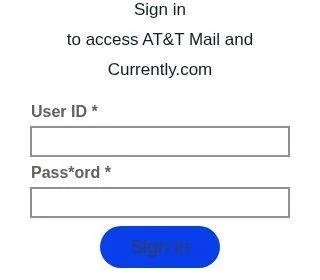
Automated URL scanner urlDNA posted on Mastodon (infosec.exchange) on 11 November 2026 that hxxps://pub-f2ec4aa4192d4950abc21ae9510403d4[.]r2[.]dev/still[.]html is a possible phishing page; the host is also on the Phishing Army blocklist. urlDNA's screenshot shows a page imitating a cPanel webmail login with the message "Your session cookie is invalid. Please log in again" and fields for an email address and email password. cPanel and Cloudflare are the services being misused and are not involved. If an email link says your mail session expired, go to your webmail directly instead of using the link.

How the scam works

Pages that copy a familiar sign-in form are usually reached from an email, text, advert, comment or search result that warns of a problem with an account, a delivery or a payment. The form looks official, but anything typed — a password, a one-time code or a wallet recovery phrase — goes to whoever set up the page rather than to the real company. Those details can be used at once to take over the account, change the recovery email or empty a wallet.

The page is hosted on a Cloudflare R2 bucket at pub-f2ec4aa4192d4950abc21ae9510403d4.r2.dev/still.html and copies a cPanel-style webmail login, including a 'session cookie is invalid' message. cPanel and Cloudflare were not the operators of this lure; a genuine host will not ask you to re-enter a mailbox password on a random r2.dev address. If you typed a password there, change it at the real mail host and at any other site that reused it, and review forwarding rules.

Source

Public post on Mastodon, 11 November 2026: https://infosec.exchange/@urldna/117598756242284905

The indicators come from this source and have not been independently checked by scammers.com.
Red flags

  • A sign-in or account page whose address is not your real mail host.
  • A message, ad or email that urges you to sign in through a link to fix a problem, pay a fee or claim a reward.
  • A request for your password, one-time login code or recovery phrase on a page you reached from a link.
  • A cPanel or your mail host name in the address or on the page that does not match the company's real website.

If you were targeted

  1. 1Do not enter passwords, card numbers or one-time codes on a page reached from a text, email or ad.
  2. 2Open the official app or type your real mail host yourself to check your account.
  3. 3If you entered details, change your password at once and contact the company through its official channels.
  4. 4Report the message and the link to the company and to your national reporting service.
  5. 5Delete the message without replying or tapping any links.
PhishingReviewed

Fake Onet Poczta (Polish webmail) login page at xxvv435.weebly.com

PhishDestroy posted on Mastodon on 12 November 2026 that xxvv435[.]weebly[.]com is a phishing page. Its record describes an Onet Poczta login page with email and password fields, flagged by 19 of 92 VirusTotal engines…

  • xxvv435.weebly.com
  • Weebly subdomain; URLScan brand: onetpl; VirusTotal 19/92
Reported Nov 12, 20261 report
PhishingReviewed

GMX.net email login phishing page at xncok12.weebly.com

PhishDestroy posted on Mastodon on 12 November 2026 that xncok12[.]weebly[.]com is a phishing page. Its record describes a GMX.NET-branded email and password login form, flagged by 17 of 92 VirusTotal engines. GMX is…

  • xncok12.weebly.com
  • Weebly subdomain; VirusTotal 17/92
Reported Nov 12, 20261 report