Skip to content
Scammers.com
Fake prize & rewardReviewed

Fake 'Hadiah Shopee' prize page at shopee-sale26.blogspot.com demands admin fee

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://shopee-sale26[.]blogspot[.]com is a confirmed scam (9 of 10). Its report describes a fake Shopee prize-winner page titled "HADIAH SHOPEE 2023" that tells…

First reported
Reports
1

Source: infosec.exchange · published

Illustration: Jobs, prizes and offers scams

What happened

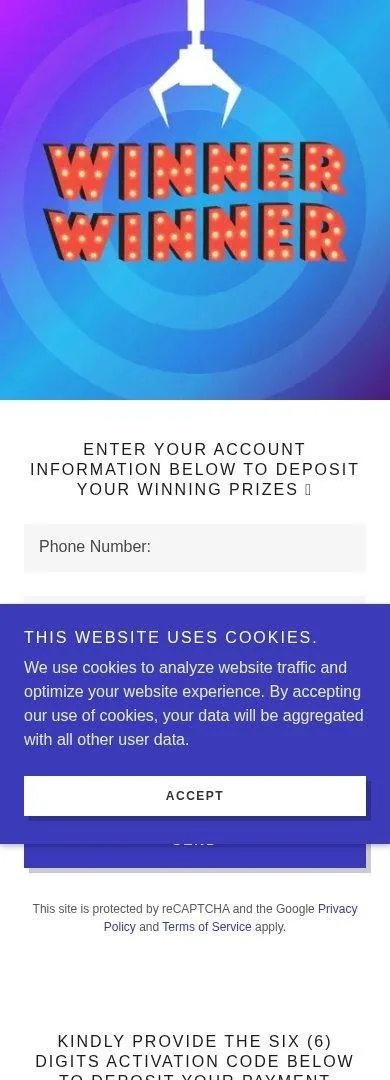
ScanMalware posted on Mastodon on 14 November 2026 that hxxps://shopee-sale26[.]blogspot[.]com is a confirmed scam (9 of 10). Its report describes a fake Shopee prize-winner page titled "HADIAH SHOPEE 2023" that tells visitors they have won a Rp 185 million prize and demands an upfront 'administration fee' before releasing it, a classic advance-fee scam; it says the lure arrives by SMS, uses secrecy and deadline pressure, and directs contact only through WhatsApp. Shopee is being impersonated and is not involved. Real prizes never require you to pay a fee first. The address is also on the Phishing Army and OpenPhish lists.

How the scam works

Impersonation schemes borrow a trusted name — a school, a police force, a bank, a well-known person or a regulator-registered firm — so that a message, a website or a phone number looks official. The real organisation is not involved and will not ask you to pay, log in or send money through a surprise link or an unlisted number. Look up the official contact details yourself and call or write there. If you have already paid or given personal information, contact your bank and report the incident to the police or your national cyber-crime service.

If a message, a page or a caller creates urgency about money, a login or a legal threat, pause and check the claim through a contact method you already trust. Keep screenshots, reference numbers and the exact addresses or phone numbers you were given, and tell your bank early if money has already left the account. Official brands and authorised firms named in a lure are not involved unless a primary source says otherwise.

Source

Source: https://infosec.exchange/@scanmalware/117614729989721878 (ScanMalware (@scanmalware@infosec.exchange), Nov 14, 2026, 7:12 AM ET)
Red flags

  • A promised high, fixed or guaranteed return, or pressure to deposit quickly after a call or a chat message.
  • A firm or website that is not on your national regulator's register, or that copies the name of a firm that is.
  • A request to pay by crypto, a bank transfer or a payment method with weak buyer protection.
  • A new domain, a clone phone number, or withdrawal delays once you try to take money out.

If you were targeted

  1. 1Check the firm and the website on your national regulator's warning list and register before you send money.
  2. 2Type official websites yourself and ignore unexpected calls, ads or Telegram pitches.
  3. 3If you already paid, contact your bank or exchange promptly and keep records of the site, chats and transfers.
  4. 4Report the firm to the regulator in your country and, if you are in the UK, to the FCA.
PhishingReviewed

Free 'Brawl Stars gems' page at trinitymax.net

PhishDestroy listed trinitymax[.]net as phishing in a post on Mastodon on 15 November 2026. Its screenshot, and urlscan.io scans the same day of hxxps://trinitymax[.]net/t/b3c711a8, show a page titled "Brawl Stars" of…

  • trinitymax.net
  • Path /t/b3c711a8, page titled 'Brawl Stars' offering 214 gems
Reported Nov 15, 20261 report
PhishingReviewed

'Contract Business Proposal – View Document' lure page on businesspropsal.weebly.com

urlDNA flagged hxxp://www[.]businesspropsal[.]weebly[.]com/ as possible phishing on Mastodon on 15 November 2026. Its screenshot shows a free Weebly page with a large PDF icon, the heading "CONTRACT BUSINESS PROPOSAL…

  • businesspropsal.weebly.com
  • Also www.businesspropsal.weebly.com; fake PDF 'View Document' button
  • Free-host phishing pages on Weebly, Firebase or web.app (15 Nov 2026 cluster)
Reported Nov 15, 20261 report
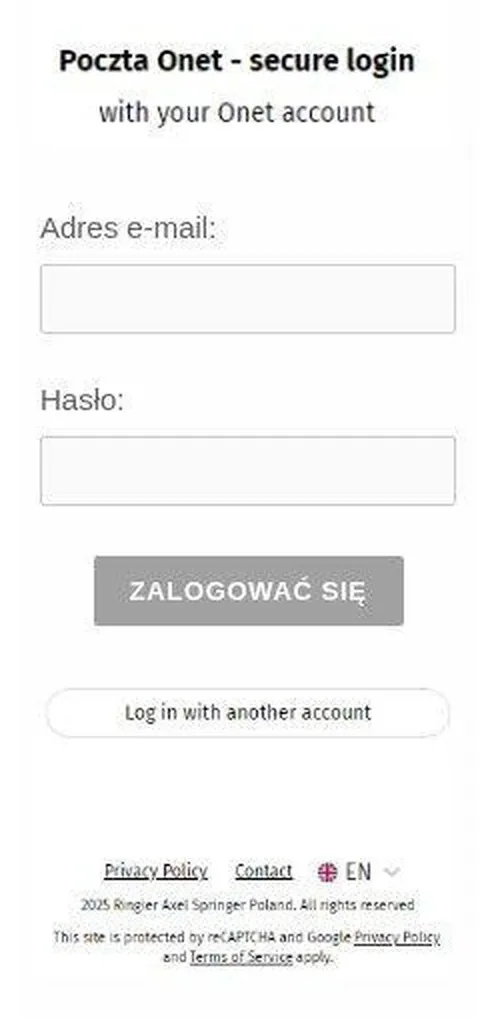
Blank email and password fields on a fake Poczta Onet secure-login page, with the Onet logo cropped out.
PhishingReviewed

Fake Onet Poczta (Polish webmail) login page on 222srrr.weebly.com

urlDNA flagged hxxps://222srrr[.]weebly[.]com as possible phishing on Mastodon on 15 November 2026. Its screenshot shows a page headed "Poczta Onet - secure login" asking for an email address and password ("Adres e-ma…

  • 222srrr.weebly.com
  • Free Weebly site with 'Poczta Onet - secure login' email + password form
  • Free-host phishing pages on Weebly, Firebase or web.app (15 Nov 2026 cluster)
Reported Nov 15, 20261 report