Skip to content
Scammers.com
Crypto, investment & PonziReviewed

Fake Trezor 'Log-In / Starting Up Your Device' page at trezor-login-us-auth-start.typedream.app

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://trezor-login-us-auth-start[.]typedream[.]app is high risk (8 of 10). Its report describes a Trezor-branded setup guide titled "Trezor Wallet Log-In - Sta…

First reported
Reports
1

Source: infosec.exchange · published

Illustration: Investing and crypto scams

What happened

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://trezor-login-us-auth-start[.]typedream[.]app is high risk (8 of 10). Its report describes a Trezor-branded setup guide titled "Trezor Wallet Log-In - Starting Up Your Device" on a Typedream subdomain, using the look-alike spelling "Trézor", with a phishing match in more than one threat-intelligence source and a high-severity network alert. It found no login form on the page itself but says to treat it as a brand-impersonation phishing lure. Trezor (SatoshiLabs) is being impersonated and is not involved. Set up Trezor devices only via trezor.io/start. The address is also on the Phishing Army phishing blocklist. Never type a recovery phrase or connect a wallet on a site reached from an ad, message or search result.

How the scam works

Crypto phishing and draining sites ask you to connect a wallet, sign a transaction, 'claim' a token, or paste a recovery phrase. Once you approve the request, the operator can empty the wallet. Address-poisoning works differently: the operator sends dust or zero-value transfers from a look-alike address so that, later, a hurried copy-paste from the transaction history goes to them instead of to the address you meant. Always check every character of an address, and never connect a wallet or enter a seed phrase on a site you reached from a message, a pop-up or a look-alike URL. Official wallet and exchange brands named in a lure are not involved.

Source

Source: https://infosec.exchange/@scanmalware/117615191809873479 (ScanMalware (@scanmalware@infosec.exchange), Nov 14, 2026, 9:10 AM ET)
Red flags

  • A site or bot that asks you to connect a wallet, sign a transaction, claim a token or paste a recovery phrase.
  • A deposit or payment address that only matches the start and end of the address you used before.
  • A 'support' or 'founder' account that writes first on Telegram, X or email and pushes a live link or a contract address.
  • A promise of a guaranteed return, a free mint or a sudden airdrop from a look-alike brand.

If you were targeted

  1. 1Never paste a seed phrase or approve a wallet connection on a site you reached from a message or a look-alike URL.
  2. 2Check every character of an address, not just the first and last digits, and confirm it in a saved official entry.
  3. 3If funds have left the wallet, stop further approvals, move what remains to a new wallet you control, and document the transaction hashes.
  4. 4Report the site, contract or account to the real project's official channels and to a blockchain-abuse desk if one exists.

Fake Trezor setup page at lear-trezorsuite.vercel.app pushes off-site software downloads

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://lear-trezorsuite[.]vercel[.]app is high risk (8 of 10). Its report says the page, titled "Trezor.io/Start | Starting Up Your Device | Trezor", copies Tre…

  • lear-trezorsuite.vercel.app
  • Vercel page titled 'Trezor.io/Start | Starting Up Your Device | Trezor'
  • Trezor-branded phishing or fake setup pages (14 Nov 2026 cluster)
Reported Nov 14, 20261 report

urlDNA flags trezor-bridge-cdn.vercel.app fake Trezor Bridge page

The urlDNA scanning service posted on Mastodon on 14 November 2026 that hxxps://trezor-bridge-cdn.vercel.app is possible phishing, linking its scan analysis. The domain also appears on the Phishing Army extended block…

  • trezor-bridge-cdn.vercel.app
  • Hosted on shared vercel.app domain
  • Trezor-branded phishing or fake setup pages (14 Nov 2026 cluster)
Reported Nov 14, 20261 report

urlDNA flags doc-exodusweb3-auth.pineapple.page fake Exodus Web3 Wallet page

The urlDNA scanning service posted on Mastodon on 15 November 2026 that hxxps://doc-exodusweb3-auth.pineapple.page is possible phishing. The page presents itself as the Exodus Web3 Wallet, using accented look-alike sp…

  • doc-exodusweb3-auth.pineapple.page
  • Hosted on shared pineapple.page site-builder domain
  • Crypto wallet phishing or drainer pages (15 Nov 2026 cluster)
Reported Nov 15, 20261 report
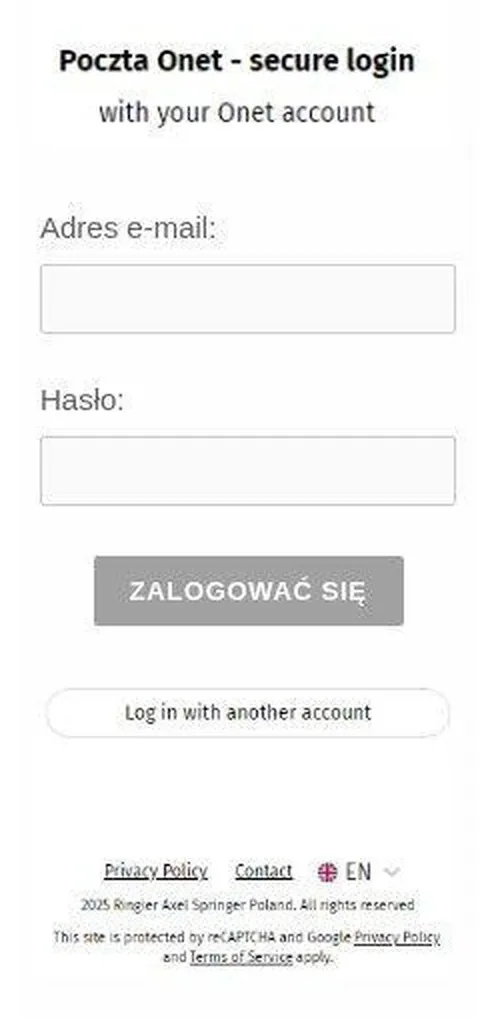
Blank email and password fields on a fake Poczta Onet secure-login page, with the Onet logo cropped out.
PhishingReviewed

Fake Onet Poczta (Polish webmail) login page on 222srrr.weebly.com

urlDNA flagged hxxps://222srrr[.]weebly[.]com as possible phishing on Mastodon on 15 November 2026. Its screenshot shows a page headed "Poczta Onet - secure login" asking for an email address and password ("Adres e-ma…

  • 222srrr.weebly.com
  • Free Weebly site with 'Poczta Onet - secure login' email + password form
  • Free-host phishing pages on Weebly, Firebase or web.app (15 Nov 2026 cluster)
Reported Nov 15, 20261 report