What happened
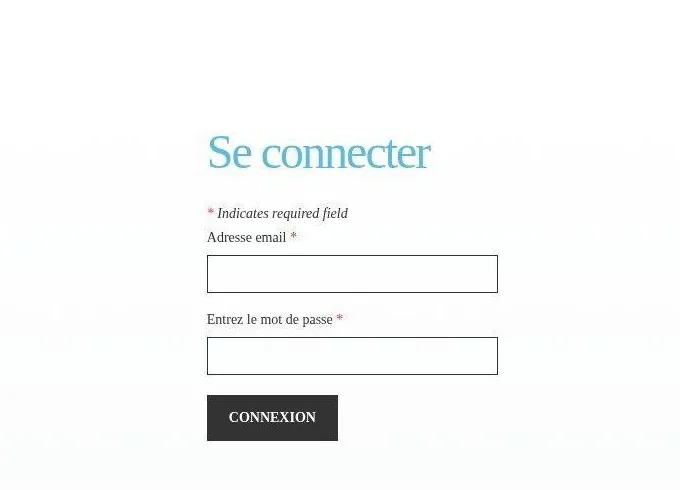
Anti-phishing project PhishDestroy posted on Mastodon on 11 November 2026 that wppoctza[.]weebly[.]com and wppkfkdpl[.]weebly[.]com are phishing detections. Its analysis pages say both show a minimal login form with a "WP poczta"-style logo (WP Poczta is a large Polish webmail service) asking for an email address and password ("Hasło"); 18 of 92 VirusTotal engines flagged each, and both are on the Phishing Army blocklist. WP and Weebly are the services being misused and are not involved. Log in to webmail only at the provider's own address, not on pages built with free site builders.
How the scam works
Pages that copy a familiar sign-in form are usually reached from an email, text, advert, comment or search result that warns of a problem with an account, a delivery or a payment. The form looks official, but anything typed — a password, a one-time code or a wallet recovery phrase — goes to whoever set up the page rather than to the real company. Those details can be used at once to take over the account, change the recovery email or empty a wallet.
wppoctza.weebly.com and wppkfkdpl.weebly.com are Weebly sites, not official WP Poczta or Wirtualna Polska mail pages. Wirtualna Polska was impersonated and is not involved. Other Weebly-hosted sign-in pages flagged the same day include a fake ALEFPA login at ago-alefpa.weebly.com and a fake mail.com 'premium update' page at mail-premium-updatess.weebly.com. Sign in to WP Poczta only through the official app or by typing the official address yourself.
Source
Public post on Mastodon, 11 November 2026: https://mastodon.social/@phishdestroy/117597467287068779
The indicators come from this source and have not been independently checked by scammers.com.