What happened
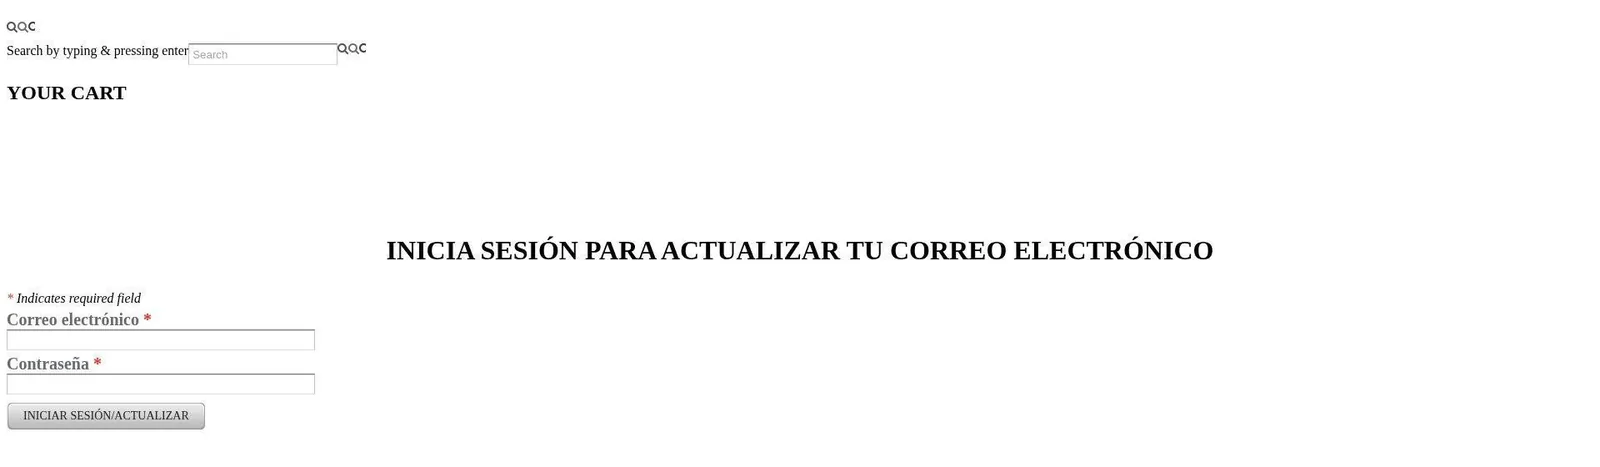
A post on X on 13 November 2026 shared a ScanMalware result rating peee-dash-zim-six[.]vercel[.]app/zimba.html a "CONFIRMED SCAM". ScanMalware's analysis describes a clone of the Zimbra Web Client sign-in page on a Vercel subdomain whose password form posts credentials to the third-party form service formsubmit.co, forwarding them to a personal email address. Zimbra, the webmail software, is being spoofed and is not involved. The domain is also on the Phishing Army blocklist. Sign in to work or university webmail only at the address your organisation provides.
How the scam works
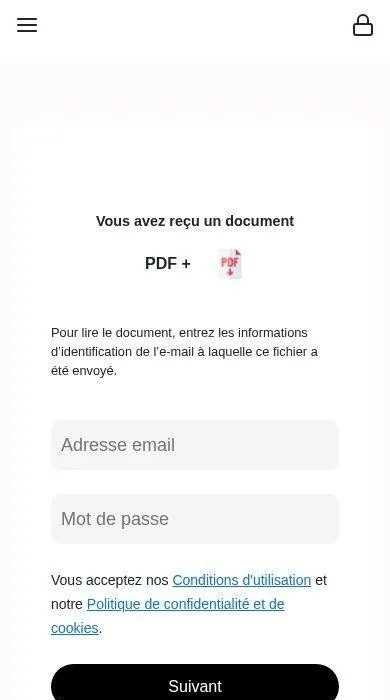
These pages copy a familiar login, payment or delivery form so that a typed password, one-time code, card number or other personal detail goes to the operator rather than to the real company. The address is often a look-alike domain, a newly registered shop, or a free host such as Weebly, Wix, Firebase, Vercel, Workers or Pages. Some kits cloak the real form from scanners and only show it in certain countries or to certain devices. The brand whose name or logo appears is being impersonated and is not involved, unless the report says the page was planted on a compromised official site, in which case only that path is the phishing lure. Open the official app or type the company's real address yourself. If you already entered a password or a card number, change the password on the official site, turn on a new two-factor method, and contact the company and your bank.
Source
Source: https://x.com/chris_uk2026/status/2121118058701873437 (@chris_uk2026 (sharing a ScanMalware result), Nov 13, 2026, 12:48 AM ET); https://scanmalware.com/result/aa12be42-9e49-492c-a030-3559dd9f76f6 (ScanMalware result, Nov 13, 2026)