Skip to content
Scammers.com
Bank & account takeoverReviewed

Florida woman Zamar McPherson gets 36 months for business email compromise scheme that diverted victims' wire payments

The U.S. Attorney's Office for the Western District of Virginia said on 13 November 2026 that Zamar McPherson, 50, of Boynton Beach, Florida, was sentenced on 12 November to 36 months in federal prison, followed by th…

First reported
Reports
1

Source: justice.gov · published

Illustration: Banking, cards and identity scams

What happened

The U.S. Attorney's Office for the Western District of Virginia said on 13 November 2026 that Zamar McPherson, 50, of Boynton Beach, Florida, was sentenced on 12 November to 36 months in federal prison, followed by three years of supervised release, for her role in a business email compromise scheme that stole millions of dollars from victims across the United States. She had pleaded guilty to one count of conspiracy to commit bank and wire fraud and two counts of wire fraud, and was ordered to forfeit $154,474.85 and to pay more than $1.5 million in restitution to four victims, jointly with co-conspirators. According to the release, victims who planned to send legitimate wire payments received new account details from fictitious email accounts created by a member of the conspiracy, and sent large sums to personal and illegitimate business accounts opened by McPherson and co-conspirators Garland Shelton, 57, of Wytheville, Virginia, and Olivia Oxley, 35, of Brooklyn, New York, who were sentenced earlier this year. HSI and the FBI announced the case with the U.S. Attorney's Office.

How the scam works

These pages copy a familiar login, payment or delivery form so that a typed password, one-time code, card number or other personal detail goes to the operator rather than to the real company. The address is often a look-alike domain, a newly registered shop, or a free host such as Weebly, Wix, Firebase, Vercel, Workers or Pages. Some kits cloak the real form from scanners and only show it in certain countries or to certain devices. The brand whose name or logo appears is being impersonated and is not involved, unless the report says the page was planted on a compromised official site, in which case only that path is the phishing lure. Open the official app or type the company's real address yourself. If you already entered a password or a card number, change the password on the official site, turn on a new two-factor method, and contact the company and your bank.

Source

Source: https://x.com/WDVAnews/status/2121254969168801870 (@WDVAnews, Nov 13, 2026, 9:52 AM ET); https://www.justice.gov/usao-wdva/pr/florida-woman-sentenced-scamming-millions-dollars-e-mail (USAO WDVA, 13 Nov 2026)
Red flags

  • A login, payment or 'verification' page on a look-alike, newly registered or free-hosting address that copies a well-known brand.
  • A message, ad or pop-up that pressures you to sign in, pay or confirm a code through a link.
  • A request for a password, a one-time or 2FA code, a card number, a government ID or a recovery phrase.
  • The real company's name or logo used on a site that is not its official address.

If you were targeted

  1. 1Do not enter passwords, codes or card details on a page you reached from an unexpected message or ad.
  2. 2Open the official app or type the company's real address yourself.
  3. 3If you already entered details, change the password on the official site, review devices and payments, and contact the company and your bank.
  4. 4Report the link to the brand and to your national cyber-crime or CERT service.

Thai SEC flags another 'CointeIegraph' lookalike Facebook page (capital I for l) for unlicensed investment business

The Securities and Exchange Commission of Thailand added a new entry to its Investor Alert list with a disclosure date of 13/11/2026 for a Facebook page named 'CointeIegraph' (spelled with a capital letter I in place…

  • Facebook page 'CointeIegraph' facebook.com/profile.php?id=61595831025582; ad library id 2806345403092704
  • Unlicensed investment solicitation warnings (13 Nov 2026)
Reported Nov 13, 20261 report
U.S. Attorney's Office Middle District of Florida press-release graphic on an Illinois man sentenced for stealing Social Security benefits

Illinois man Jonathan Barner sentenced to 15 months for taking $107K in his dead grandmother's Social Security benefits

The U.S. Attorney's Office for the Middle District of Florida said on 13 November 2026 that Jonathan Frank Barner, 55, of Illinois, was sentenced by a U.S. District Judge to 15 months in federal prison for theft of go…

  • Jonathan Frank Barner, 55, Illinois; Social Security retirement benefits of a deceased beneficiary
Reported Nov 13, 20261 report
U.S. Department of War Office of Inspector General Defense Criminal Investigative Service graphic

Florida man Chad Monroe pleads guilty to $42M Medicare brace and cancer genetic-testing fraud and a PPP loan fraud

The U.S. Justice Department said on 13 November 2026 that Chad Monroe, 48, of Tarpon Springs, Florida, pleaded guilty that day to one count of conspiracy to commit health care fraud and one count of wire fraud over a…

  • Chad Monroe, Tarpon Springs FL; Maksix Medical Products; Orthotech Atlanta; 1st Choice Medical Supply
  • Medicare durable-medical-equipment or telemedicine fraud (13 Nov 2026)
Reported Nov 13, 20261 report
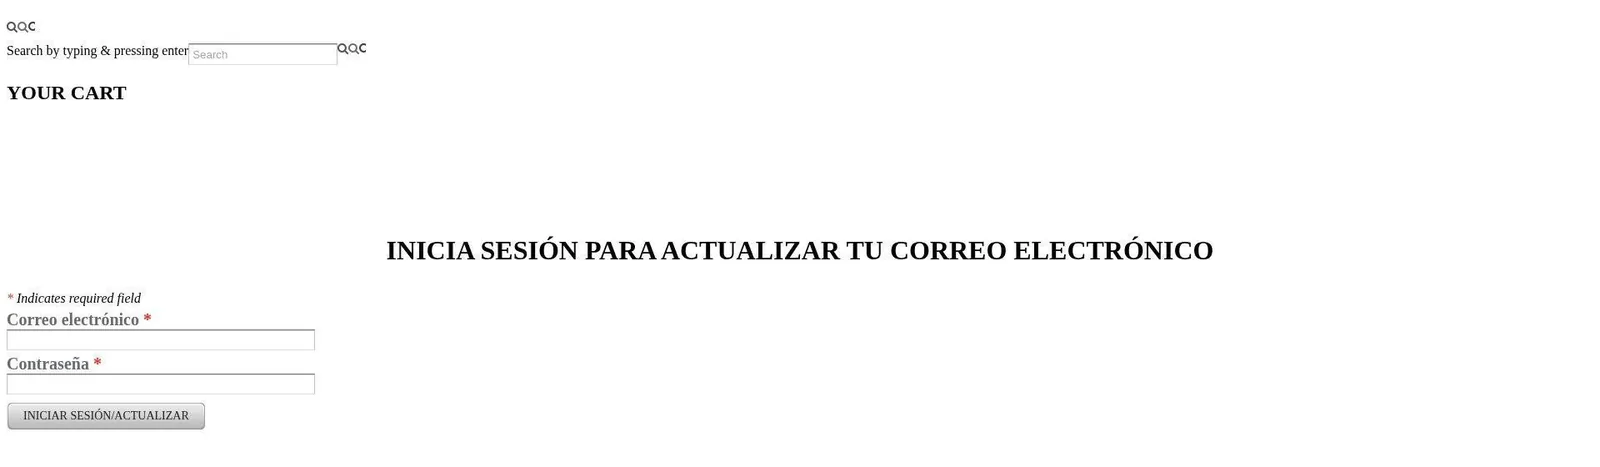
Screenshot of a Spanish-language fake 'sign in to update your email' page with empty email and password fields
PhishingReviewed

Spanish 'sign in to update your email' credential page at correo2026.weebly.com

urlDNA flagged hxxps://correo2026[.]weebly[.]com as possible phishing on Mastodon on 13 November 2026. Its screenshot shows a Spanish-language page headed "Inicia sesión para actualizar tu correo electrónico" (sign in…

  • correo2026.weebly.com
  • Weebly subdomain; form 'Inicia sesión para actualizar tu correo electrónico'
  • Weebly-hosted phishing pages (13 Nov 2026 cluster)
Reported Nov 13, 20261 report