'Messages on hold' email phishing uses fake webmail login at gsnameansmei.wixsite.com
PCrisk reports a phishing email posing as an automated notice from the recipient's email provider, titled "Email failure to receive messages". It claims four messages are on hold, says the domain will be restricted wi…
- First reported
- Reports
- 1
Source: pcrisk.com · published
What happened
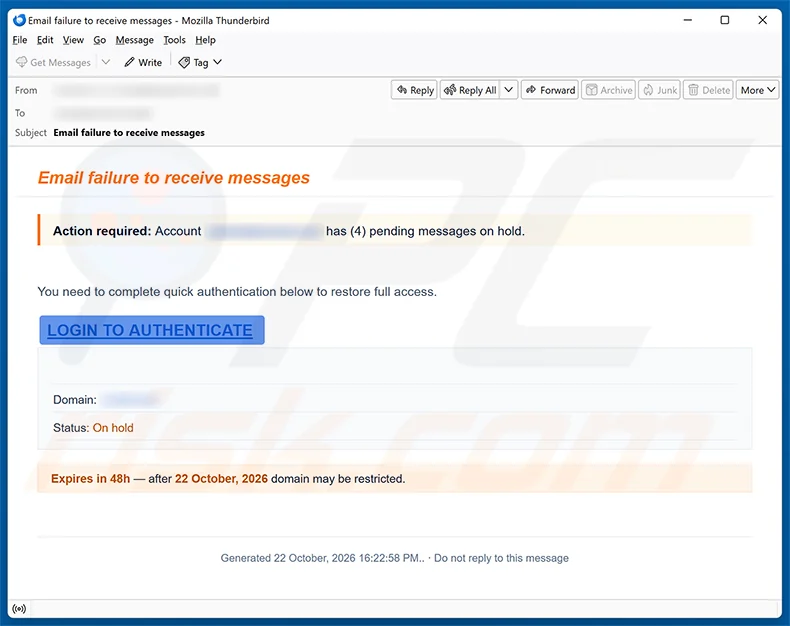
PCrisk reports a phishing email posing as an automated notice from the recipient's email provider, titled "Email failure to receive messages". It claims four messages are on hold, says the domain will be restricted within 48 hours unless the user clicks "LOGIN TO AUTHENTICATE", and carries a "Generated 22 October 2026" footer. The button opens a fake webmail login page on the Wix site gsnameansmei.wixsite.com, including a "Log in via cPanelID" option, and submitted email passwords go to the scammers. Wix and legitimate email or hosting providers are not accused: the site is a free page that someone has abused. The message gives the account and domain names, which are blurred in the sample.
How the scam works
This is a standard mailbox-quota or held-message lure. It claims that messages the recipient has not yet seen are waiting, which creates a fear of missing something important, and it adds a 48-hour deadline with the threat that the domain "may be restricted". The "authenticate" button points to a page built on a free Wix site, not to the real email host.
The fake page copies a webmail login, with a cPanel-style option, to suit small businesses whose email is run through web hosting. Anything typed in is passed to the operator. A stolen mailbox password gives access to the account's mail, can be used for password resets and lets attackers impersonate the owner in messages to customers and colleagues.
PCrisk's conclusion is that this is a phishing scam disguised as an alert from an email service provider, built to capture email credentials that scammers then use to hijack accounts and potentially access other services. The message should be ignored and deleted. A real provider's notice about held mail will not ask you to log in through a link in the email; open your webmail or control panel by typing its address yourself.
PCrisk notes that campaigns of this kind are sometimes also used to distribute malware, rather than or in addition to harvesting credentials, so a click should never be treated as harmless.
Source
PCrisk, "Email Failure To Receive Messages Scam" (removal guide, 27 October 2026).
Red flags
- An 'automated' email saying messages are on hold and a deadline of 48 hours.
- A threat that your domain will be restricted if you don't log in.
- A 'login to authenticate' button that leads to a free-website address (here a wixsite.com page).
- A login page offering odd options such as 'Log in via cPanelID'.
- A generic sender with no real name, and a 'do not reply' footer.
If you were targeted
- 1Don't click the button or log in through the email; open your webmail or hosting panel by typing its address yourself.
- 2If you entered your password, change it immediately and check your mailbox for forwarding rules.
- 3Turn on multi-factor authentication and look at recent sign-in activity.
- 4Report the email as phishing to your provider or IT team, then delete it.
- 5Warn colleagues if it reached a shared domain.