Skip to content
Scammers.com
PhishingReviewed

Meta-support-styled page bussiness-metasupports.pages.dev hides stealer code, Telegram exfiltration

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://bussiness-metasupports[.]pages[.]dev is high risk (8 of 10). Its report says the free pages.dev subdomain, named to look like Meta business support, serv…

First reported
Reports
1

Source: infosec.exchange · published

Illustration: Phishing, texts and email scams

What happened

ScanMalware posted on Mastodon on 14 November 2026 that hxxps://bussiness-metasupports[.]pages[.]dev is high risk (8 of 10). Its report says the free pages.dev subdomain, named to look like Meta business support, serves a bare 'Privacy Policy' shell that hides credential-stealing JavaScript matching a critical hunting rule and a Telegram bot token used to send stolen data, plus anti-DevTools evasion, and then instantly redirects to a Google 404 page. Fake 'Meta Business Support' pages are a common lure against Facebook and Instagram page owners. Meta is being spoofed and is not involved; Cloudflare Pages is only the host. The address is also on the Phishing Army phishing blocklist.

How the scam works

These pages copy a familiar login, payment or delivery form so that a typed password, one-time code, card number or other personal detail goes to the operator rather than to the real company. The address is often a look-alike domain, a newly registered shop, or a free host such as Weebly, Wix, Firebase, Vercel, Workers or Pages. Some kits cloak the real form from scanners and only show it in certain countries or to certain devices. The brand whose name or logo appears is being impersonated and is not involved, unless the report says the page was planted on a compromised official site, in which case only that path is the phishing lure. Open the official app or type the company's real address yourself. If you already entered a password or a card number, change the password on the official site, turn on a new two-factor method, and contact the company and your bank.

Source

Source: https://infosec.exchange/@scanmalware/117616457353424716 (ScanMalware (@scanmalware@infosec.exchange), Nov 14, 2026, 2:31 PM ET)
Red flags

  • A login, payment or 'verification' page on a look-alike, newly registered or free-hosting address that copies a well-known brand.
  • A message, ad or pop-up that pressures you to sign in, pay or confirm a code through a link.
  • A request for a password, a one-time or 2FA code, a card number, a government ID or a recovery phrase.
  • The real company's name or logo used on a site that is not its official address.

If you were targeted

  1. 1Do not enter passwords, codes or card details on a page you reached from an unexpected message or ad.
  2. 2Open the official app or type the company's real address yourself.
  3. 3If you already entered details, change the password on the official site, review devices and payments, and contact the company and your bank.
  4. 4Report the link to the brand and to your national cyber-crime or CERT service.
PhishingReviewed

Free 'Brawl Stars gems' page at trinitymax.net

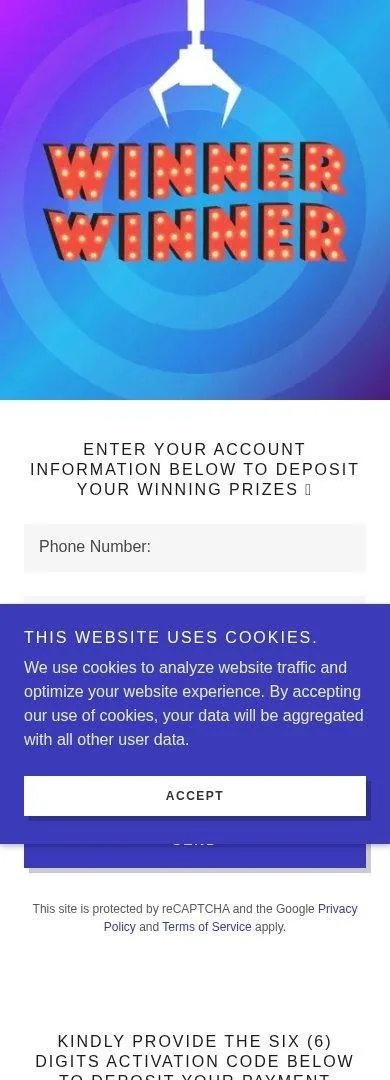
PhishDestroy listed trinitymax[.]net as phishing in a post on Mastodon on 15 November 2026. Its screenshot, and urlscan.io scans the same day of hxxps://trinitymax[.]net/t/b3c711a8, show a page titled "Brawl Stars" of…

  • trinitymax.net
  • Path /t/b3c711a8, page titled 'Brawl Stars' offering 214 gems
Reported Nov 15, 20261 report
PhishingReviewed

'Contract Business Proposal – View Document' lure page on businesspropsal.weebly.com

urlDNA flagged hxxp://www[.]businesspropsal[.]weebly[.]com/ as possible phishing on Mastodon on 15 November 2026. Its screenshot shows a free Weebly page with a large PDF icon, the heading "CONTRACT BUSINESS PROPOSAL…

  • businesspropsal.weebly.com
  • Also www.businesspropsal.weebly.com; fake PDF 'View Document' button
  • Free-host phishing pages on Weebly, Firebase or web.app (15 Nov 2026 cluster)
Reported Nov 15, 20261 report
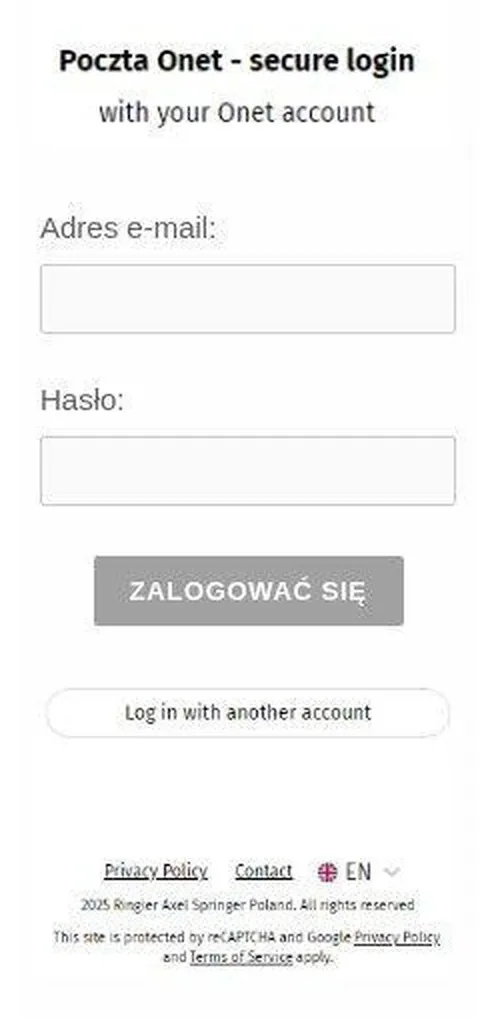
Blank email and password fields on a fake Poczta Onet secure-login page, with the Onet logo cropped out.
PhishingReviewed

Fake Onet Poczta (Polish webmail) login page on 222srrr.weebly.com

urlDNA flagged hxxps://222srrr[.]weebly[.]com as possible phishing on Mastodon on 15 November 2026. Its screenshot shows a page headed "Poczta Onet - secure login" asking for an email address and password ("Adres e-ma…

  • 222srrr.weebly.com
  • Free Weebly site with 'Poczta Onet - secure login' email + password form
  • Free-host phishing pages on Weebly, Firebase or web.app (15 Nov 2026 cluster)
Reported Nov 15, 20261 report
Blank Username, E-Mail and Password fields from a fake Outlook Web App sign-in form, with the Outlook logo cropped out.
PhishingReviewed

Fake 'Outlook Web App' sign-in page at srva.closer.website

urlDNA flagged hxxp://www[.]srva[.]closer[.]website/ as possible phishing in a post on Mastodon on 15 November 2026. Its screenshot shows a copy of the Microsoft "Outlook Web App" sign-in screen with fields for a doma…

  • srva.closer.website
  • Also reached as www.srva.closer.website; Outlook Web App-style form (domain, username, password)
  • Outlook-branded password phishing pages (15 Nov 2026 cluster)
Reported Nov 15, 20261 report