What happened
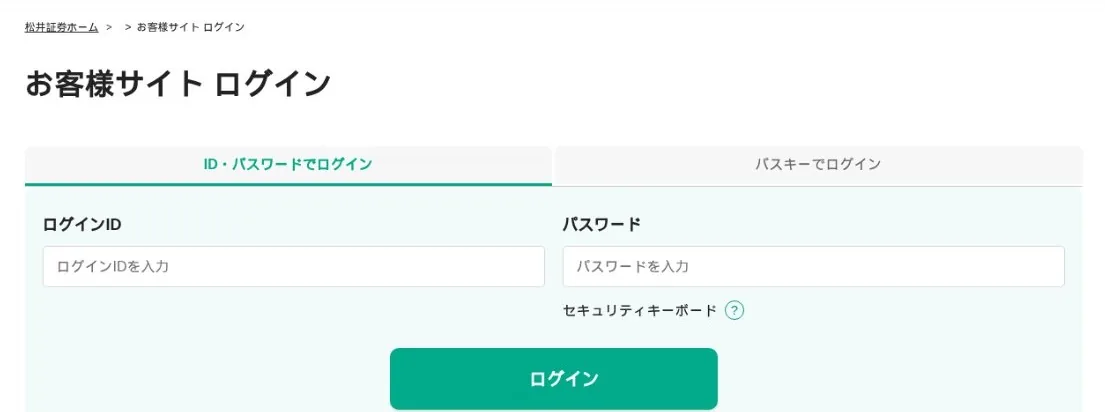
The Metemcyber account posted on X on 11 November 2026, with credit to Team NA4Sec, a phishing site targeting Japan that impersonates Matsui Securities (松井証券), the Japanese online brokerage, at hxxps://orvexilium[.]cfd/drgsdfbdr/#/index, hosted at IP 8.211.162.242 (ASN AS45102). Matsui Securities is impersonated and is not the operator. Log in to brokerage accounts only through the official app or a bookmarked address.
How the scam works
Pages that copy a familiar sign-in form are usually reached from an email, text, advert, comment or search result that warns of a problem with an account, a delivery or a payment. The form looks official, but anything typed — a password, a one-time code or a wallet recovery phrase — goes to whoever set up the page rather than to the real company. Those details can be used at once to take over the account, change the recovery email or empty a wallet.
The page at orvexilium.cfd, on the path /drgsdfbdr/#/index, copies a Matsui Securities customer login form. Matsui Securities was impersonated and is not involved. The same research team also flagged nuvexalora.cfd on the same IP address, 8.211.162.242, with the same path, as another copy of that login page. Sign in to Matsui only through the official site or app you already use, not from a link in a message.
Matsui Securities does not move its customer login to a .cfd domain. If you already typed a password on orvexilium.cfd, change it on the official site from a device you trust and review recent sign-ins.
Source
Public post on X, 11 November 2026: https://x.com/Metemcyber/status/2120402911171936594
The indicators come from this source and have not been independently checked by scammers.com.