Skip to content
Scammers.com
PhishingReviewed

Researcher lists 17 .cn '/verify/' sites spreading malware posing as Sumitomo Mitsui Card

Security researcher @KesaGataMe0 posted on X on 12 November 2026 a list of sites labeled as malware distribution impersonating SMBC / SMCC / Sumitomo Mitsui Card (三井住友カード), all at IP 8.216.50.3 (AS45102, Alibaba (US)…

First reported
Reports
1

Source: x.com · published

Illustration: Phishing, texts and email scams

What happened

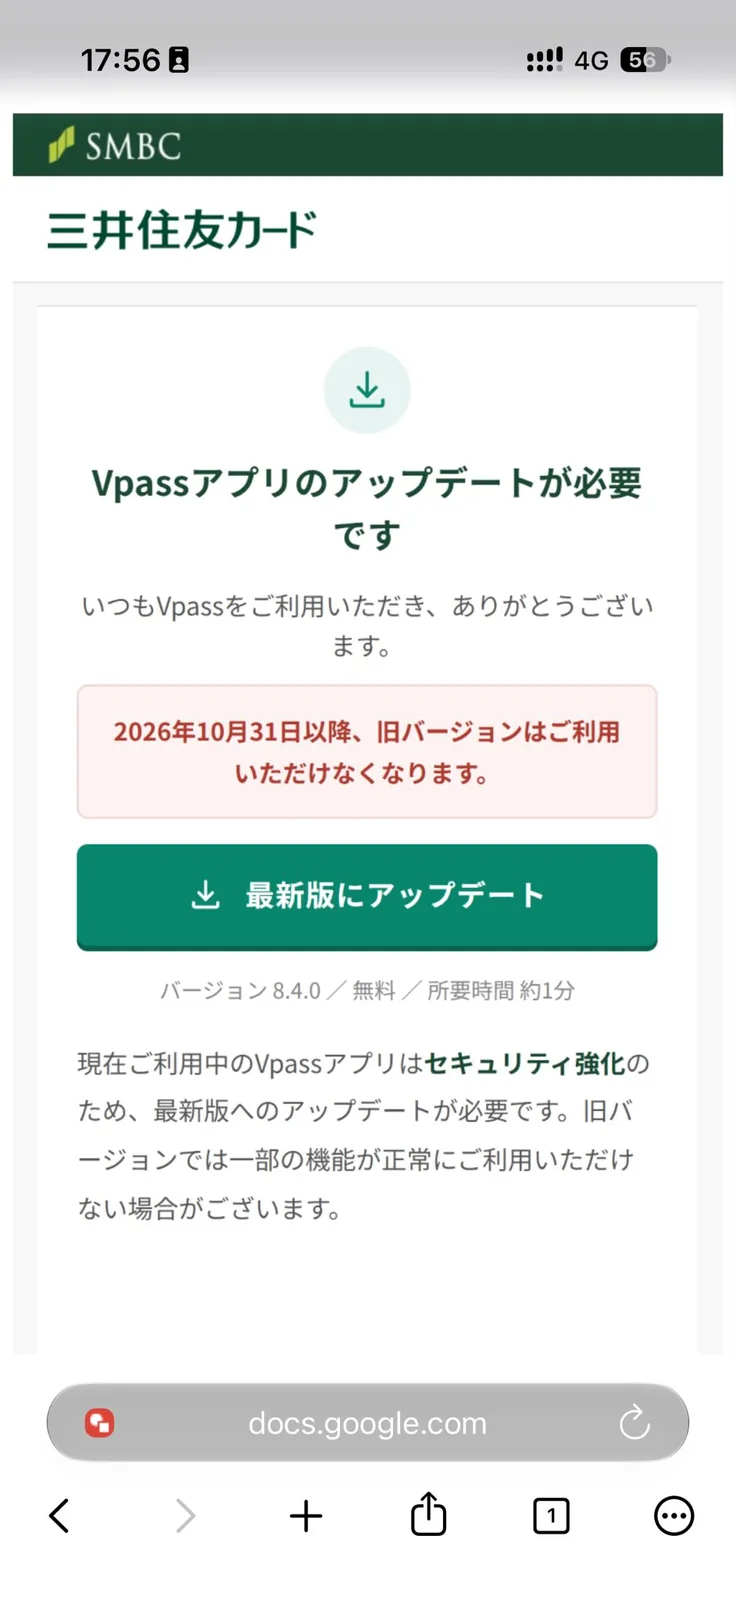
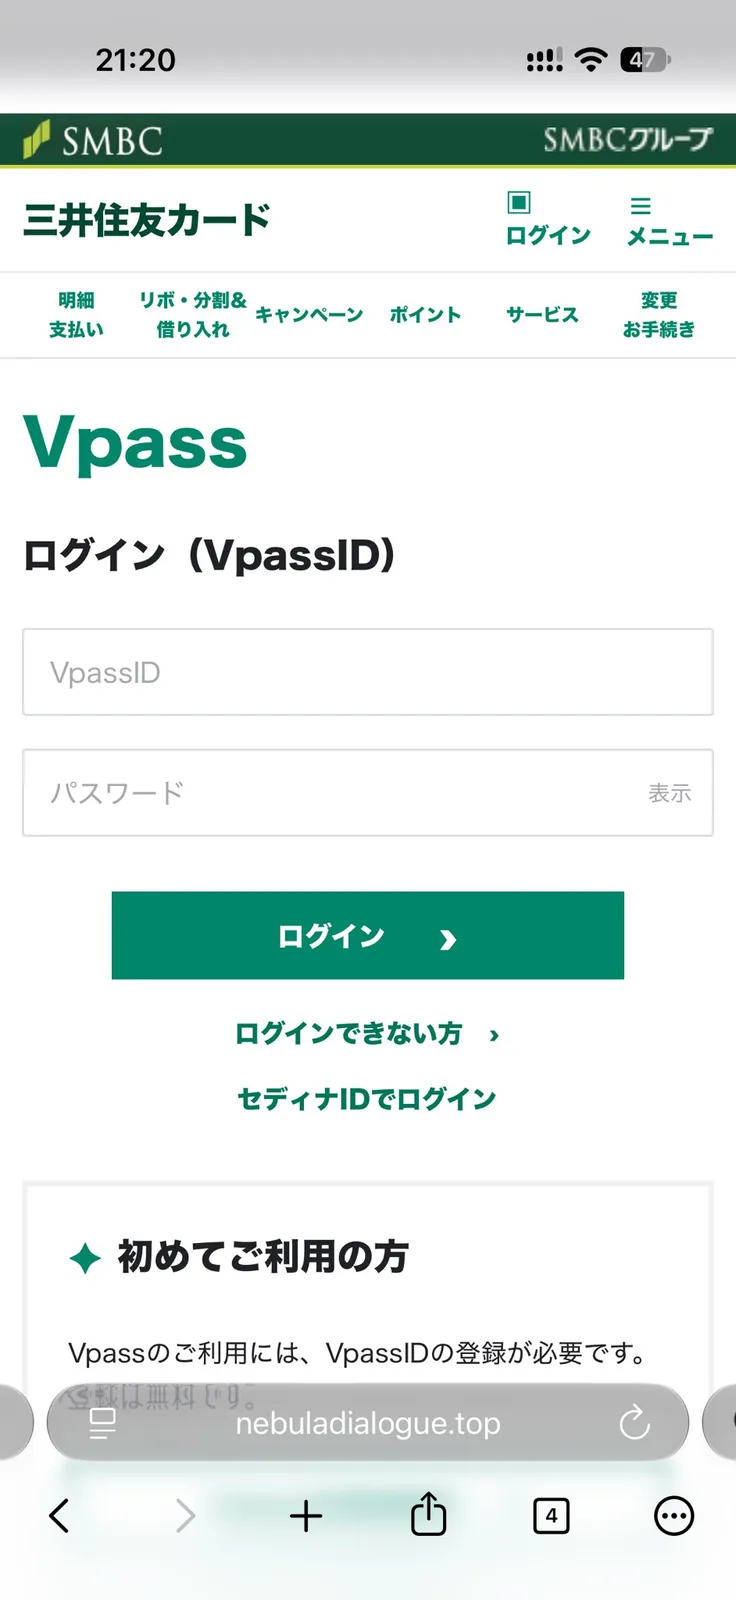
Security researcher @KesaGataMe0 posted on X on 12 November 2026 a list of sites labeled as malware distribution impersonating SMBC / SMCC / Sumitomo Mitsui Card (三井住友カード), all at IP 8.216.50.3 (AS45102, Alibaba (US) Technology Co., Ltd.) and using a /verify/ path. The domains listed are: suxsygr.cn, qgfhduc.cn, vjqerpg.cn, hqipdvj.cn, vdfcwwx.cn, nxykfic.cn, dcrudyf.cn, yhtpktl.cn, zthktzx.cn, bqodpaz.cn, sbqfyfc.cn, qqvuomqt.cn, dwzrfue.cn, azfdlwt.cn, ekyhkrmt.cn, mutfsdg.cn and refhigy.cn. In an earlier post the same day the researcher also flagged nzxaxcj.cn/verify/ redirecting to /verify/update.html on the same IP. Sumitomo Mitsui Card and SMBC are impersonated and are not the operators. Do not install apps or 'updates' from links in messages; get apps only from official app stores. Source: https://x.com/KesaGataMe0/status/2120870102661050504

How the scam works

These pages copy a familiar login, payment or delivery form so that a typed password, one-time code, card number or other personal detail goes to the operator rather than to the real company. The address is often a look-alike domain, a newly registered shop, or a free host such as Weebly, Wix, Firebase, Vercel, Workers or Pages. Some kits cloak the real form from scanners and only show it in certain countries or to certain devices. The brand whose name or logo appears is being impersonated and is not involved, unless the report says the page was planted on a compromised official site, in which case only that path is the phishing lure. Open the official app or type the company's real address yourself. If you already entered a password or a card number, change the password on the official site, turn on a new two-factor method, and contact the company and your bank.

Source

Source: https://x.com/KesaGataMe0/status/2120870102661050504
Red flags

  • A login, payment or 'verification' page on a look-alike, newly registered or free-hosting address that copies a well-known brand.
  • A message, ad or pop-up that pressures you to sign in, pay or confirm a code through a link.
  • A request for a password, a one-time or 2FA code, a card number, a government ID or a recovery phrase.
  • The real company's name or logo used on a site that is not its official address.

If you were targeted

  1. 1Do not enter passwords, codes or card details on a page you reached from an unexpected message or ad.
  2. 2Open the official app or type the company's real address yourself.
  3. 3If you already entered details, change the password on the official site, review devices and payments, and contact the company and your bank.
  4. 4Report the link to the brand and to your national cyber-crime or CERT service.

MalwareTips: mssstock.com's Million Securities claims SEC adviser licence; SEC lists it as exempt, not registered

MalwareTips published an investigation today into Million Securities, which presents mssstock.com as a stock trading platform with wealth management and investment banking services, and whose press releases (distribut…

  • mssstock.com
  • Earlier press-release domain coinln.com; SEC CRD 338838 (Exempt Reporting Adviser, not registered)
  • Unauthorised / AI-trading investment sites flagged 12 Nov 2026
Reported Nov 12, 20261 report