Resecurity maps Iron Man phishing kit infrastructure domains
Resecurity mapped the infrastructure of "Iron Man System", a phishing kit sold to criminals with 2,360 lure templates impersonating couriers, tax agencies, banks and more across 130 countries.
- First reported
- Reports
- 1
Source: resecurity.com · published
What happened
Resecurity published research on October 14, 2026 on "Iron Man System", a commercial phishing-kit-as-a-service. It is sold to criminal buyers as a self-hosted package with pre-built lure pages impersonating postal and courier services, toll and traffic-fine authorities, tax agencies, banks, telecoms and loyalty programmes. Resecurity worked with Microsoft, which led the disruption.
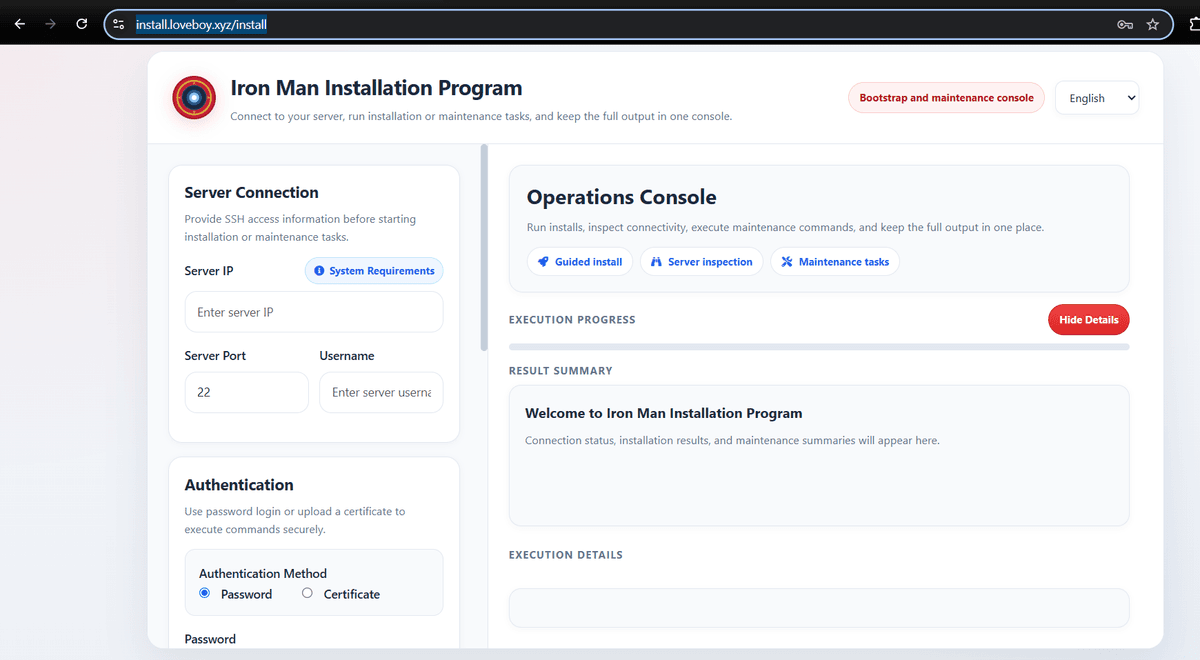
Infrastructure Resecurity listed includes the licensing backend api2.peaceman.cc, telemetry host log2.peaceloving.xyz, object storage at ossapi.haoeryu.top, and build registry and deployment hosts docker.aidchildren.cc, docker.loveboy.xyz and install.loveboy.xyz.
How the scam works
Buyers run a bilingual Chinese/English admin panel to manage lure pages, each tied to an impersonated brand, on a subscription licence. Resecurity bought a licence and ran the kit in a lab to trace its backend.
The catalogue held 2,360 distinct lure packages across 130 countries and areas, updated as recently as October 1, 2026. Courier and postal impersonation is the largest category, followed by tax-authority and banking lures. Captured victim records store a goods selection alongside payment data.
Resecurity found 911 published build versions, indicating active development and sales.
Source
Resecurity, "Iron Man & YamStore: Powering a Global Phishing-as-a-Service Ecosystem" (October 14, 2026).
Red flags
- Texts or emails about an undelivered parcel, unpaid toll, traffic fine or tax refund.
- Requests to pay a small fee by card to release a delivery or settle a fine.
- Links to sites that are not the official agency or company domain.
If you were targeted
- 1Don't follow links in unexpected delivery, toll or fine messages; go to the official site yourself.
- 2If you entered card details, call your bank to block the card.
- 3Report the message to your mobile carrier (in the US, forward to 7726) and to the FTC at ReportFraud.ftc.gov.