Skip to content
Scammers.com
PhishingReviewed

Fake Google Chrome download site at www-google-vipp.com

urlDNA flagged hxxps://www-google-vipp[.]com as possible phishing on Mastodon on 13 November 2026. Its screenshot shows a page imitating the Google Chrome download site, with the Chrome logo and download buttons, on a…

First reported
Reports
1

Source: infosec.exchange · published

Illustration: Phishing, texts and email scams

What happened

urlDNA flagged hxxps://www-google-vipp[.]com as possible phishing on Mastodon on 13 November 2026. Its screenshot shows a page imitating the Google Chrome download site, with the Chrome logo and download buttons, on a domain built to look like a Google address. Fake browser download pages are commonly used to deliver malware. Google is being spoofed and is not involved. Download Chrome only from google.com/chrome. The domain is also on the Phishing Army blocklist.

How the scam works

These pages copy a familiar login, payment or delivery form so that a typed password, one-time code, card number or other personal detail goes to the operator rather than to the real company. The address is often a look-alike domain, a newly registered shop, or a free host such as Weebly, Wix, Firebase, Vercel, Workers or Pages. Some kits cloak the real form from scanners and only show it in certain countries or to certain devices. The brand whose name or logo appears is being impersonated and is not involved, unless the report says the page was planted on a compromised official site, in which case only that path is the phishing lure. Open the official app or type the company's real address yourself. If you already entered a password or a card number, change the password on the official site, turn on a new two-factor method, and contact the company and your bank.

If a message, a page or a caller creates urgency about money, a login or a legal threat, pause and check the claim through a contact method you already trust. Keep screenshots, reference numbers and the exact addresses or phone numbers you were given, and tell your bank early if money has already left the account. Official brands and authorised firms named in a lure are not involved unless a primary source says otherwise.

Source

Source: https://infosec.exchange/@urldna/117608902807623756 (urlDNA (@urldna@infosec.exchange), Nov 13, 2026, 6:30 AM ET)
Red flags

  • A login, payment or 'verification' page on a look-alike, newly registered or free-hosting address that copies a well-known brand.
  • A message, ad or pop-up that pressures you to sign in, pay or confirm a code through a link.
  • A request for a password, a one-time or 2FA code, a card number, a government ID or a recovery phrase.
  • The real company's name or logo used on a site that is not its official address.

If you were targeted

  1. 1Do not enter passwords, codes or card details on a page you reached from an unexpected message or ad.
  2. 2Open the official app or type the company's real address yourself.
  3. 3If you already entered details, change the password on the official site, review devices and payments, and contact the company and your bank.
  4. 4Report the link to the brand and to your national cyber-crime or CERT service.
PhishingReviewed

Fake 'GTA 6 EXE download' on Google Colab delivers WARDEN Stealer that steals crypto wallets; C2 uroker.casa

Help Net Security reported today on research by Cynet into a fake 'GTA 6 EXE file download' promoted from a Google Colab notebook. The link led to a page called 'Windows Software Hub' showing a version number, downloa…

  • uroker.casa
  • Probable C2 named by Cynet; lure: Google Colab notebook -> 'Windows Software Hub' page -> ZIP with loader
  • Fake GTA VI or GTA 6 download and key-lure sites
Reported Nov 13, 20261 report
PhishingReviewed

Fake Chase 'Document Center' at chase-acess.vercel.app pushes macro-enabled file download

Web scanner ScanMalware posted on X on 13 November 2026 that chase-acess[.]vercel[.]app is a "CONFIRMED SCAM". Its analysis describes a fake Chase "Document Center" on a lookalike Vercel subdomain that lures visitors…

  • chase-acess.vercel.app
  • Vercel subdomain; page title copies 'Chase Savings Accounts: Compare & Apply Today | Chase'
  • Vercel.app-hosted phishing pages (13 Nov 2026 cluster)
Reported Nov 13, 20261 report
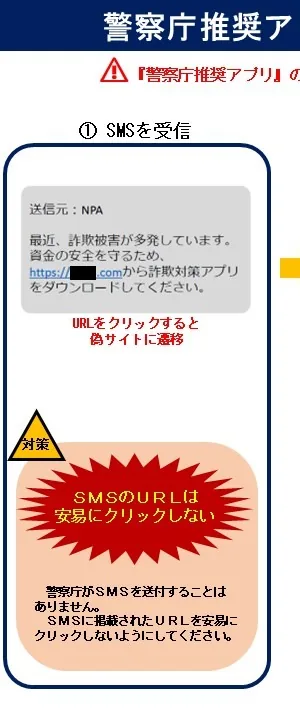
Japanese police warning graphic about SMS from 'NPA' pushing a fake police-recommended anti-fraud app, with the lure URL redacted

Japan police warn of SMS from 'NPA' pushing fake police-recommended anti-fraud app download

Japanese police accounts, including Noda Police (@NodaPolice110), warned on X on 13 November 2026 about text messages that use the sender name "NPA" (National Police Agency) and claim that fraud is on the rise, urging…

  • SMS sender name 'NPA'; fake APK posing as '詐欺対策 by NTTタウンページ' (NTT Town Page anti-fraud app)
  • Fake Japanese police or National Police Agency lure (13 Nov 2026)
Reported Nov 13, 20261 report
PhishingReviewed

Fake Zimbra webmail sign-in at peee-dash-zim-six.vercel.app sends passwords to a form service

A post on X on 13 November 2026 shared a ScanMalware result rating peee-dash-zim-six[.]vercel[.]app/zimba.html a "CONFIRMED SCAM". ScanMalware's analysis describes a clone of the Zimbra Web Client sign-in page on a Ve…

  • peee-dash-zim-six.vercel.app
  • Path /zimba.html; credentials posted to formsubmit.co
  • Webmail or email-account credential phishing (13 Nov 2026)
Reported Nov 13, 20261 report
PhishingReviewed

Firebase redirect stub track-lx92f9.firebaseapp.com sends visitors to bank, post and customs phishing kit

ScanMalware posted on X on 13 November 2026 that track-lx92f9[.]firebaseapp[.]com is a "CONFIRMED SCAM". Its analysis says the Firebase page is an empty stub that automatically redirects visitors to a Codeanywhere dev…

  • track-lx92f9.firebaseapp.com
  • Redirects to port-3000-2986758970-lasybug6855273.codeanyapp.com (Codeanywhere container)
  • Firebase or web.app-hosted phishing pages (13 Nov 2026 cluster)
Reported Nov 13, 20261 report
PhishingReviewed

BT-branded 'click here to continue' page at free-5493597.webadorsite.com

urlDNA flagged hxxps://free-5493597[.]webadorsite[.]com as possible phishing on Mastodon on 13 November 2026. Its screenshot shows a free Webador website carrying the BT logo with a "CLICK HERE TO CONTINUE" button, a…

  • free-5493597.webadorsite.com
  • Free Webador site showing BT logo and 'CLICK HERE TO CONTINUE' button
  • BT-branded email or account phishing (13 Nov 2026)
Reported Nov 13, 20261 report