MalwareTips says Patowin.com, registered one day before its check and built on a known scam site kit, is a fake crypto casino that locks winnings behind a 'verification deposit'.
patowin.com
Same site kit as cashplay.cc, riftano.com, zosanx.com and zelowin.com
MalwareTips says Nationalcasino.casino, registered one day before its check, is a fake crypto casino that credits a big bonus and then demands a 'verification deposit' before any withdrawal.
nationalcasino.casino
Same site kit as winorax.cc, patowin.com, cashplay.cc and riftano.com
MalwareTips says month-old Riftano.com is a fake crypto casino from the zosanx/zelowin kit that locks bonus balances behind crypto 'verification deposits'.
riftano.com
Same site kit as zosanx.com, zelowin.com, casxov.com, jetvos.com
MalwareTips says five-day-old Rainbetcasino.tech is a fake crypto casino from the membets.pw kit; it is not an official Rainbet site and Rainbet is not implicated.
rainbetcasino.tech
Same site kit as mgmwins.pw, slxwin.com, membets.pw, mgmresorts.pw
MalwareTips says two-week-old Bevawin.com is a fake crypto casino from the zabowex/renubet kit that locks bonus balances behind crypto 'verification deposits'.
bevawin.com
Same site kit as zabowex.com, renubet.com, raonax.win, mrbeastsgames.net
MalwareTips says Spinrun.top is a fake crypto casino that uses false celebrity claims and big promo-code bonuses, then demands a deposit before any withdrawal.
MalwareTips says Membets.pw is a newly registered fake crypto casino copied from a known scam kit, which demands a 'verification' deposit before withdrawals; MGM-named copycat domains in the same kit are not MGM's.
membets.pw
Same site kit as mgmresorts.pw, mgmwin.pw, mgmlasvegas.cc, casino-usa.info (per MalwareTips; not affiliated with MGM Resorts)
Norway's Finanstilsynet warns that Fondavex has contacted Norwegian investors offering investment services through the unauthorised trading platform steinvault.com.
Hackers hijacked An Garda Síochána's @GardaInfo X account, renamed it @HelpXaman and used it to post fake Xaman XRP 'allocation' offers; Gardaí warned the public not to interact.
X handle @HelpXaman (hijacked account); fake Xaman 'Claim your XRP allocation' airdrop posts
Security firm ExVul says a malicious EIP-7702 delegation let an attacker drain 9.1231 ETH (about $22,770) and TAPEETH tokens from an Ethereum wallet; the delegation stayed active afterwards.
Pony.ai says fraudulent websites (some using "aiponyhk" domains) and Telegram accounts are misusing its name to pitch fake crypto investments. The company offers no investment products.
Foil described a wallet-drainer farm at airdrop-memecoins.netlify.app promoted by newly created X accounts posting fake airdrops with made-up contract addresses.
Foil warned that two "Accred ($CRED) Giveaway" clones at robinhood-main-dex-vtp.netlify.app and robinhood-main-dex-eqi.netlify.app drain wallets on approval.
Foil warned that claims-memecoin.netlify.app pushes a fake "Credible Finance airdrop" for $CRED with a fake contract, and told users not to connect wallets or sign.
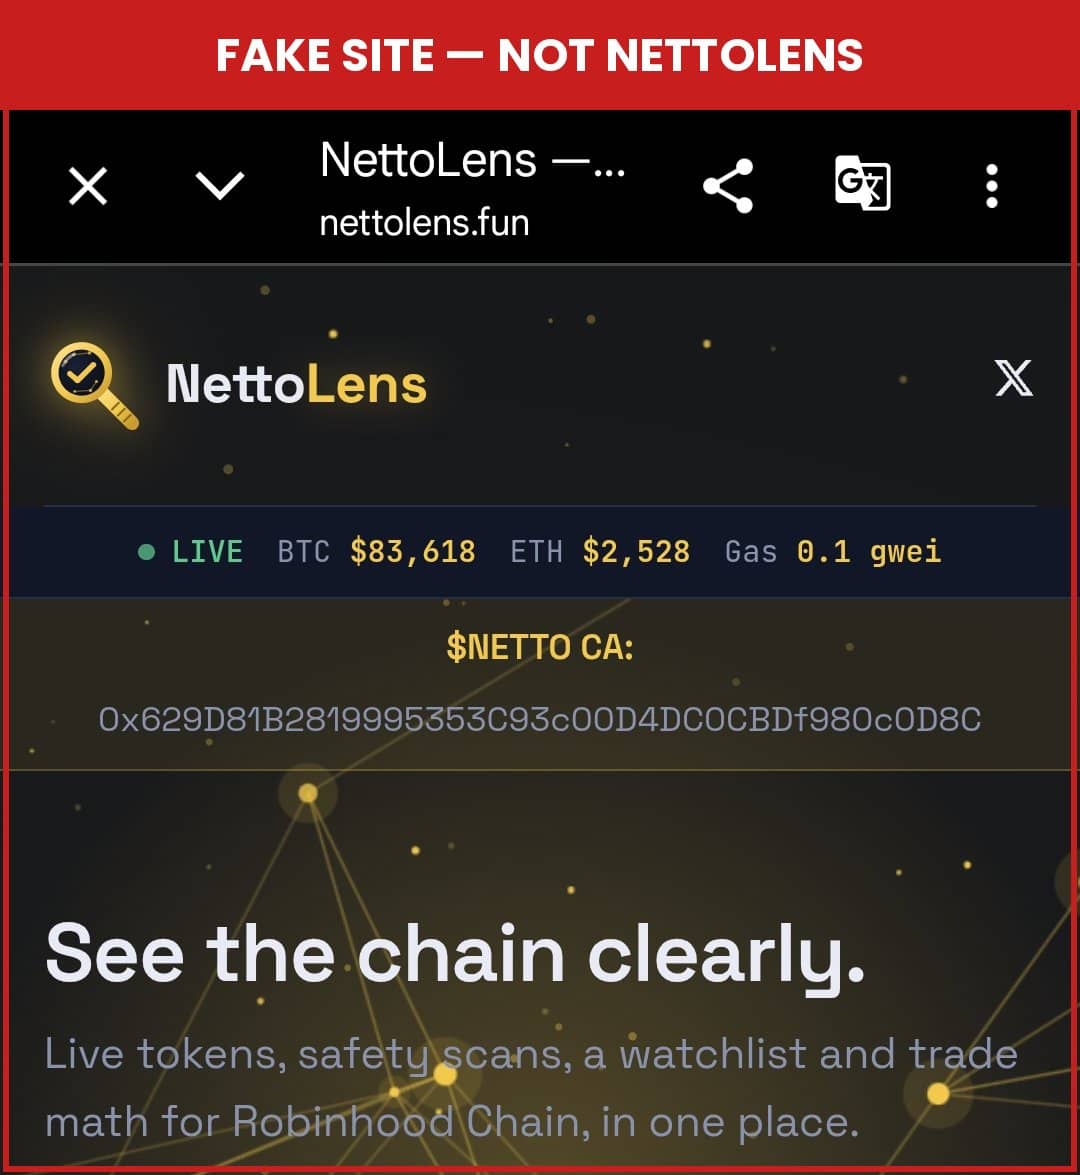
Crypto tool NettoLens warned that @NettoLensRH and nettolens.fun copied its site and logo, and that a circulating token contract (0x629D…0D8C) is fake: it has not launched a token.
Infoblox Threat Intel detailed Noir, a crypto wallet-drainer kit that looks up its current infrastructure through DNS TXT records at _r.noir.black and steals through wallet approvals rather than seed phrases.
Scam Sniffer added airdrop-checker-l2.io to its blocklist as a wallet drainer on October 13, 2026. Airdrop "eligibility checkers" hide malicious approvals inside a normal-looking claim flow.
Scam Sniffer listed app-uniswap-fi.net, a lookalike of the Uniswap app, as a wallet drainer on October 13, 2026. The real Uniswap web app is at app.uniswap.org.
Crypto security service Scam Sniffer added claim-rewards-eigen.xyz to its blocklist on October 13, 2026 and classified it as a wallet drainer that uses Eigen-style reward branding.
Elastic Security Labs found a fake Web3 accelerator called Apex that lured crypto founders with free AI credits and audits, then spread Windows and macOS malware through two malicious npm packages.