Hong Kong Interbank Clearing (HKICL) warns that fasterpaymentsystemfps.xyz is a fake "Buyer Online Protection" site for FPS payments that collects ID documents and bank details.
A Dismislab investigation found a fake Indian Visa Application Centre site, app.ivcabd.com, sent by SMS to Bangladeshi applicants, used a Tk9 "verification" fee to link and drain bKash wallets.
Jet2 warned on X that the account @Jet2tweets__h is fake and not affiliated with Jet2holidays; its only official account is @jet2tweets with a gold tick.
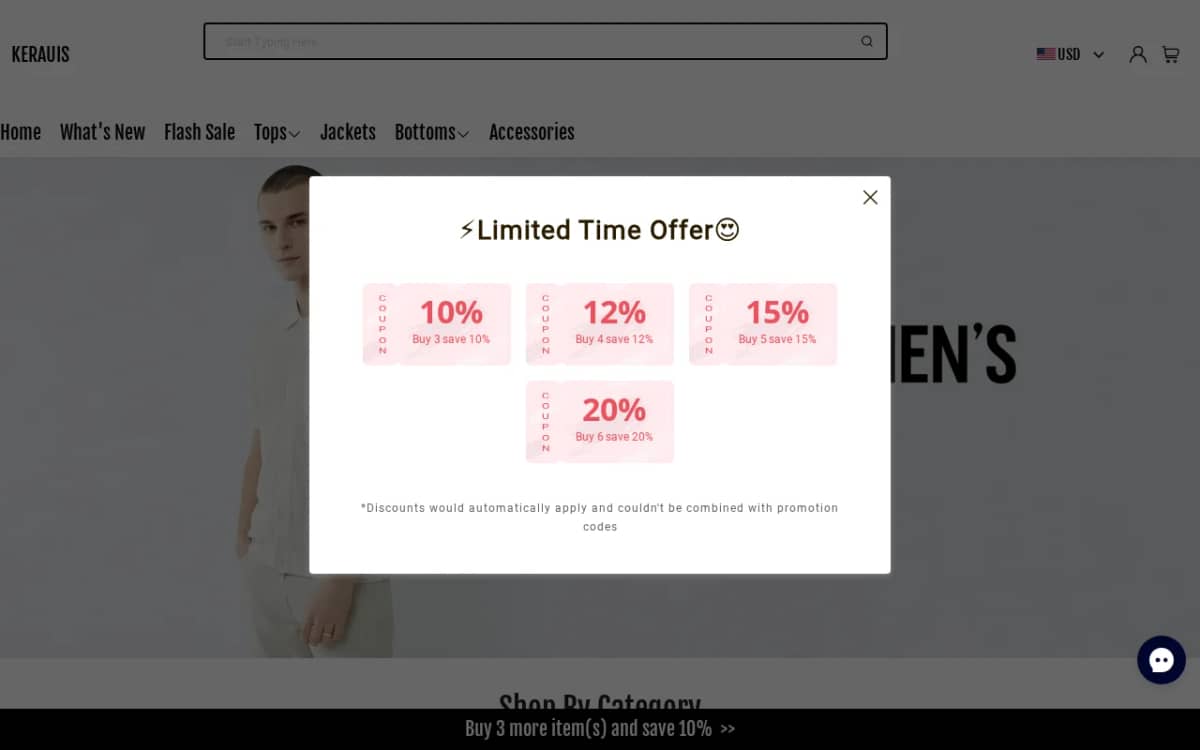
MalwareTips exposed Kerauis.com on October 14, 2026 as a fake online store advertising steep discounts on social media, with buyers receiving nothing or cheap substitutes.
MalwareTips exposed Astrongful.com on October 14, 2026 as a fake online store advertising steep discounts on social media, with buyers receiving nothing or cheap substitutes.
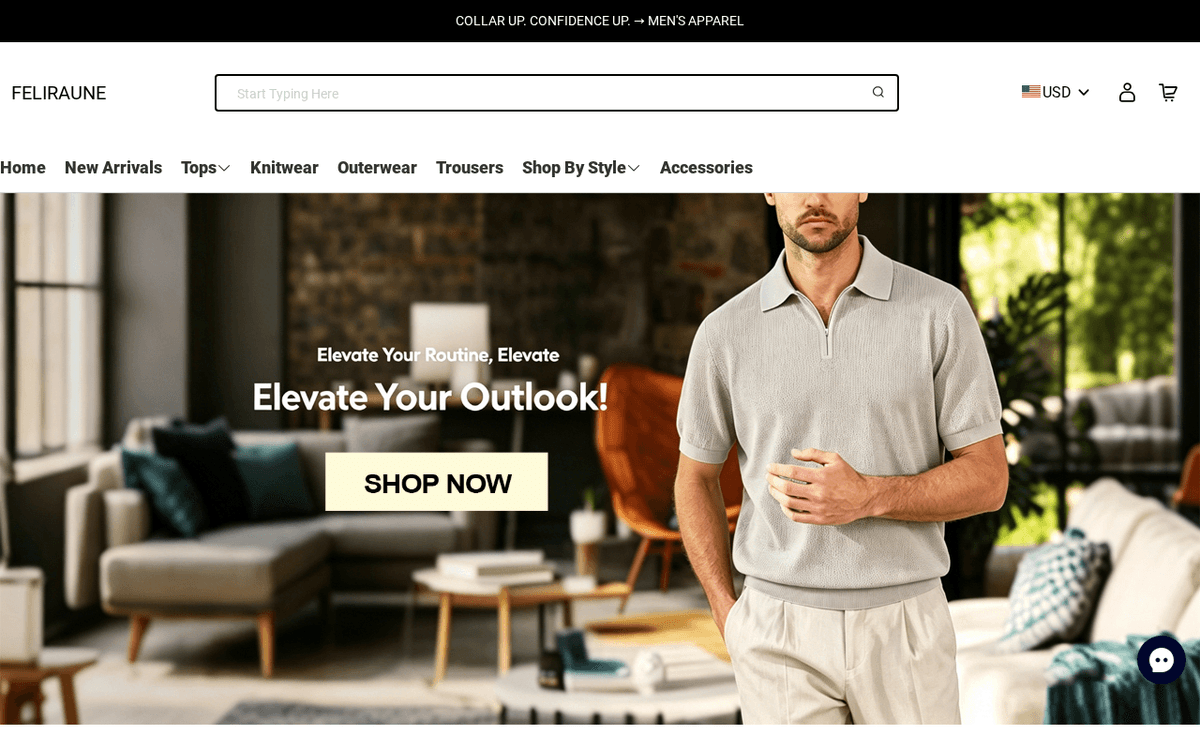
MalwareTips exposed Feliraune.com on October 14, 2026 as a fake online store advertising steep discounts on social media, with buyers receiving nothing or cheap substitutes.
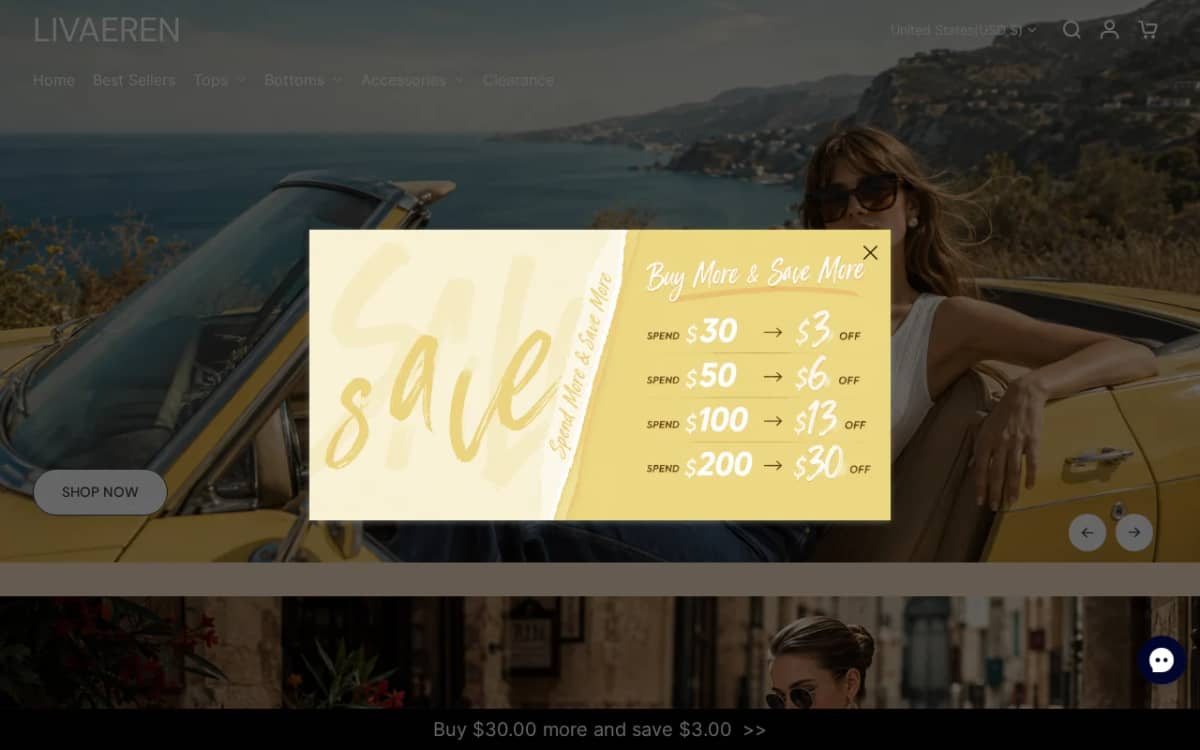
MalwareTips exposed Livaeren.com on October 14, 2026 as a fake online store advertising steep discounts on social media, with buyers receiving nothing or cheap substitutes.
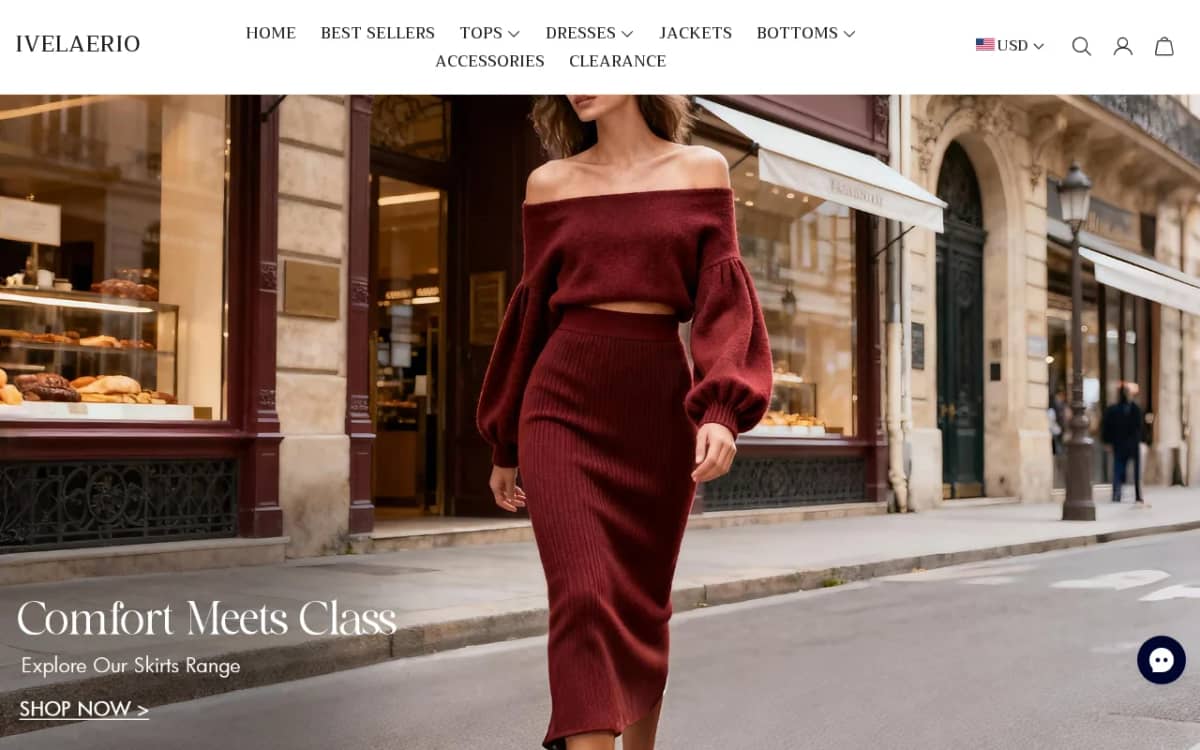
MalwareTips exposed Ivelaerio.com on October 14, 2026 as a fake online store advertising steep discounts on social media, with buyers receiving nothing or cheap substitutes.
South Africa's FSCA warns that someone using the name "Lucas Ludka", falsely claiming to be an FSCA lawyer, is offering fake grant-fund refunds over WhatsApp from 372 5616 2589.
372 5616 2589
Name used by impersonator: 'Lucas Ludka' (does not work for the FSCA)
South Africa's FSCA warns that Sappi Online Investment, a Telegram scheme promising unrealistic returns, is unauthorised and is misusing Sanlam Life's FSP number 45741.
MalwareTips warns of a "Security Center" email claiming your password is about to expire; its "Keep My Current Password" button led to a fake Gmail login on an edgeone.dev subdomain.
vocational-white-5xciizxu.edgeone.dev
Security Center Password Expiring Soon phishing campaign
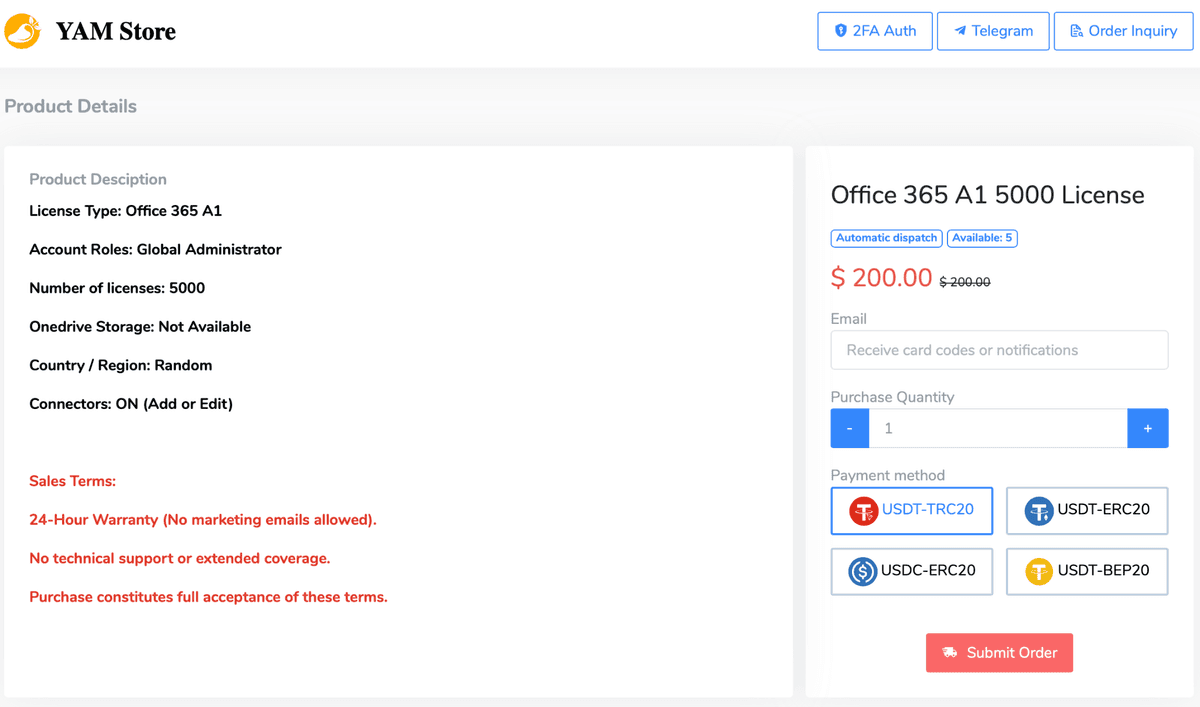
Cloudflare and Microsoft disrupted Yam Store, a Chinese-language marketplace selling stolen Microsoft business accounts and phishing kits (CoGui and Iron Man) via Telegram.
yam.ink
Yam Store Telegram sales channel; phishing kits CoGui and Iron Man
Security firm ExVul says a malicious EIP-7702 delegation let an attacker drain 9.1231 ETH (about $22,770) and TAPEETH tokens from an Ethereum wallet; the delegation stayed active afterwards.
Pony.ai says fraudulent websites (some using "aiponyhk" domains) and Telegram accounts are misusing its name to pitch fake crypto investments. The company offers no investment products.
Hong Kong's Judiciary warned of emails from spoofed @pt.lu addresses that falsely claim to come from the District Court Registrar and attach fake summonses; real summonses are never sent by email.
Thai police say ETO TH, an app and website (eto-th.com) presented as a stock trading platform, was fake; 39 people were arrested and assets worth more than 500 million baht seized or frozen.
Germany's financial regulator BaFin warned that fidus-capital.com may be offering banking, financial and crypto services without authorisation, and that it falsely uses FIDUS Finanz AG's identity.
An Inverness GP practice warned of fake NHS emails, sent from a spoofed admin@business.ro address, telling patients to download an "NHS e-signature app" and sign in with their NHS number.
Ledger said covert chips in some Ledger wallets sold by Southeast Asian reseller CryptoBilis captured users' recovery phrases and sent them out over LTE; researchers estimate up to $93.2 million stolen.
The FTC alleges Ohio-based Digital Forensics Corporation took at least $60 million from panicked sextortion victims for help it didn't provide; a court has temporarily halted the business.
Push Security found Google search ads routed through Bing redirects sending people searching "claude mac" to claude-desk-code.com, a fake Claude download page that copies a malicious command.
Proofpoint identified a website for a "BIOTOLD" biotech conference at Boston's Omni Seaport hotel (listed Nov. 5–6, 2026) as fake: a front for a criminal malware group.
Huntress found a phishing campaign, active since September 10, that hides lures on Microsoft's Power BI site and installs rogue ScreenConnect remote-access clients from the hamham27 tenant.
Pope County, Arkansas, deputies warn of calls from a fake "Lt. Brian Hill" at 470-908-2745 claiming a federal warrant and demanding 10% of the warrant amount by phone.
Foil described a wallet-drainer farm at airdrop-memecoins.netlify.app promoted by newly created X accounts posting fake airdrops with made-up contract addresses.
Foil warned that two "Accred ($CRED) Giveaway" clones at robinhood-main-dex-vtp.netlify.app and robinhood-main-dex-eqi.netlify.app drain wallets on approval.
Foil warned that claims-memecoin.netlify.app pushes a fake "Credible Finance airdrop" for $CRED with a fake contract, and told users not to connect wallets or sign.
A user in Spain reported a text pretending to be from Spain's Social Security (INSS) offering €305.85 "pending to collect", linking to the fake site portalsilofgob.top.
CyberPulse reported a fake SAPO Mail login page at login-sapomail-pt.weebly.com that tries to collect Portuguese users' emails, phone numbers and passwords.